Administrator's Guide
This guide is for Confluence Site Admins (and delegated admins) responsible for configuring and managing Content Retention Manager for Confluence.
Warning
We recommend trying our app on a development, test, or staging tenant first to familiarize yourself with the features and capabilities. This will help make sure the app conforms to your policies and expectations.
Prerequisites
- Familiarity with Retention Statuses and Discoverability in How It Works.
- A defined company policy on data retention or information governance, which you'll use to configure policies, classifications, and rules in Content Retention Manager for Confluence.
- An active Confluence Cloud instance.
- A user account with Confluence Admin (Site-Admin) privileges, or delegated admin access granted by a Confluence Admin. Confluence Admin privileges are required for installation and delegation settings only. Delegated admins can configure policies, classification, and automation, and manage content.
Installation
Install Content Retention Manager for Confluence from the Atlassian Marketplace onto your Confluence instance. Installation requires Confluence Admin privileges and cannot be performed by delegated admins.
Upgrading
Minor version updates are rolled out automatically and require no action on your part. When a new major version becomes available, you will see an in-app notification. See the Release Notes for details on new features, improvements, and bug fixes, then follow the upgrade instructions below.
To upgrade:
- In the Confluence top-level menu, navigate to Apps > Manage Apps.
- Find Content Retention Manager for Confluence in the list and click View app details.
- On the app details page, click Update to install the latest version.

Content Retention Manager for Confluence in the app list

App details page with the Update button
Accessing Content Retention Manager
In the Confluence left side navigation, select Apps, then select Content Retention Manager. Standard edition is available to all users; Lite edition restricts access to admins only.
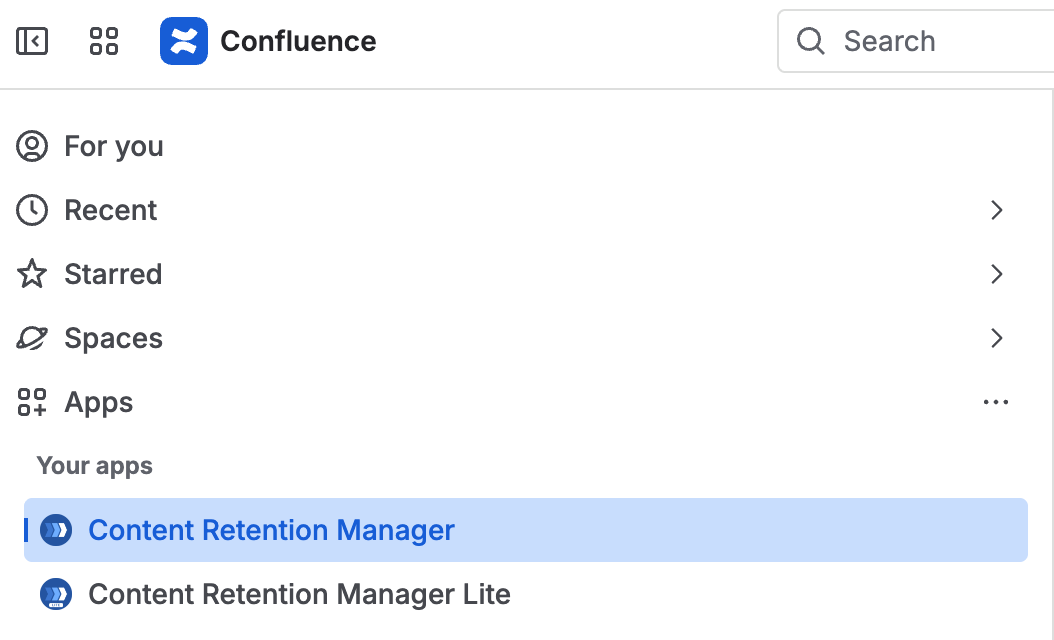
Opening Content Retention Manager from the Confluence Apps menu
Dashboard
The Dashboard provides a visual summary of your content retention status in Confluence. It gives administrators a quick view of retention coverage, policy distribution, classification levels, and upcoming expirations.
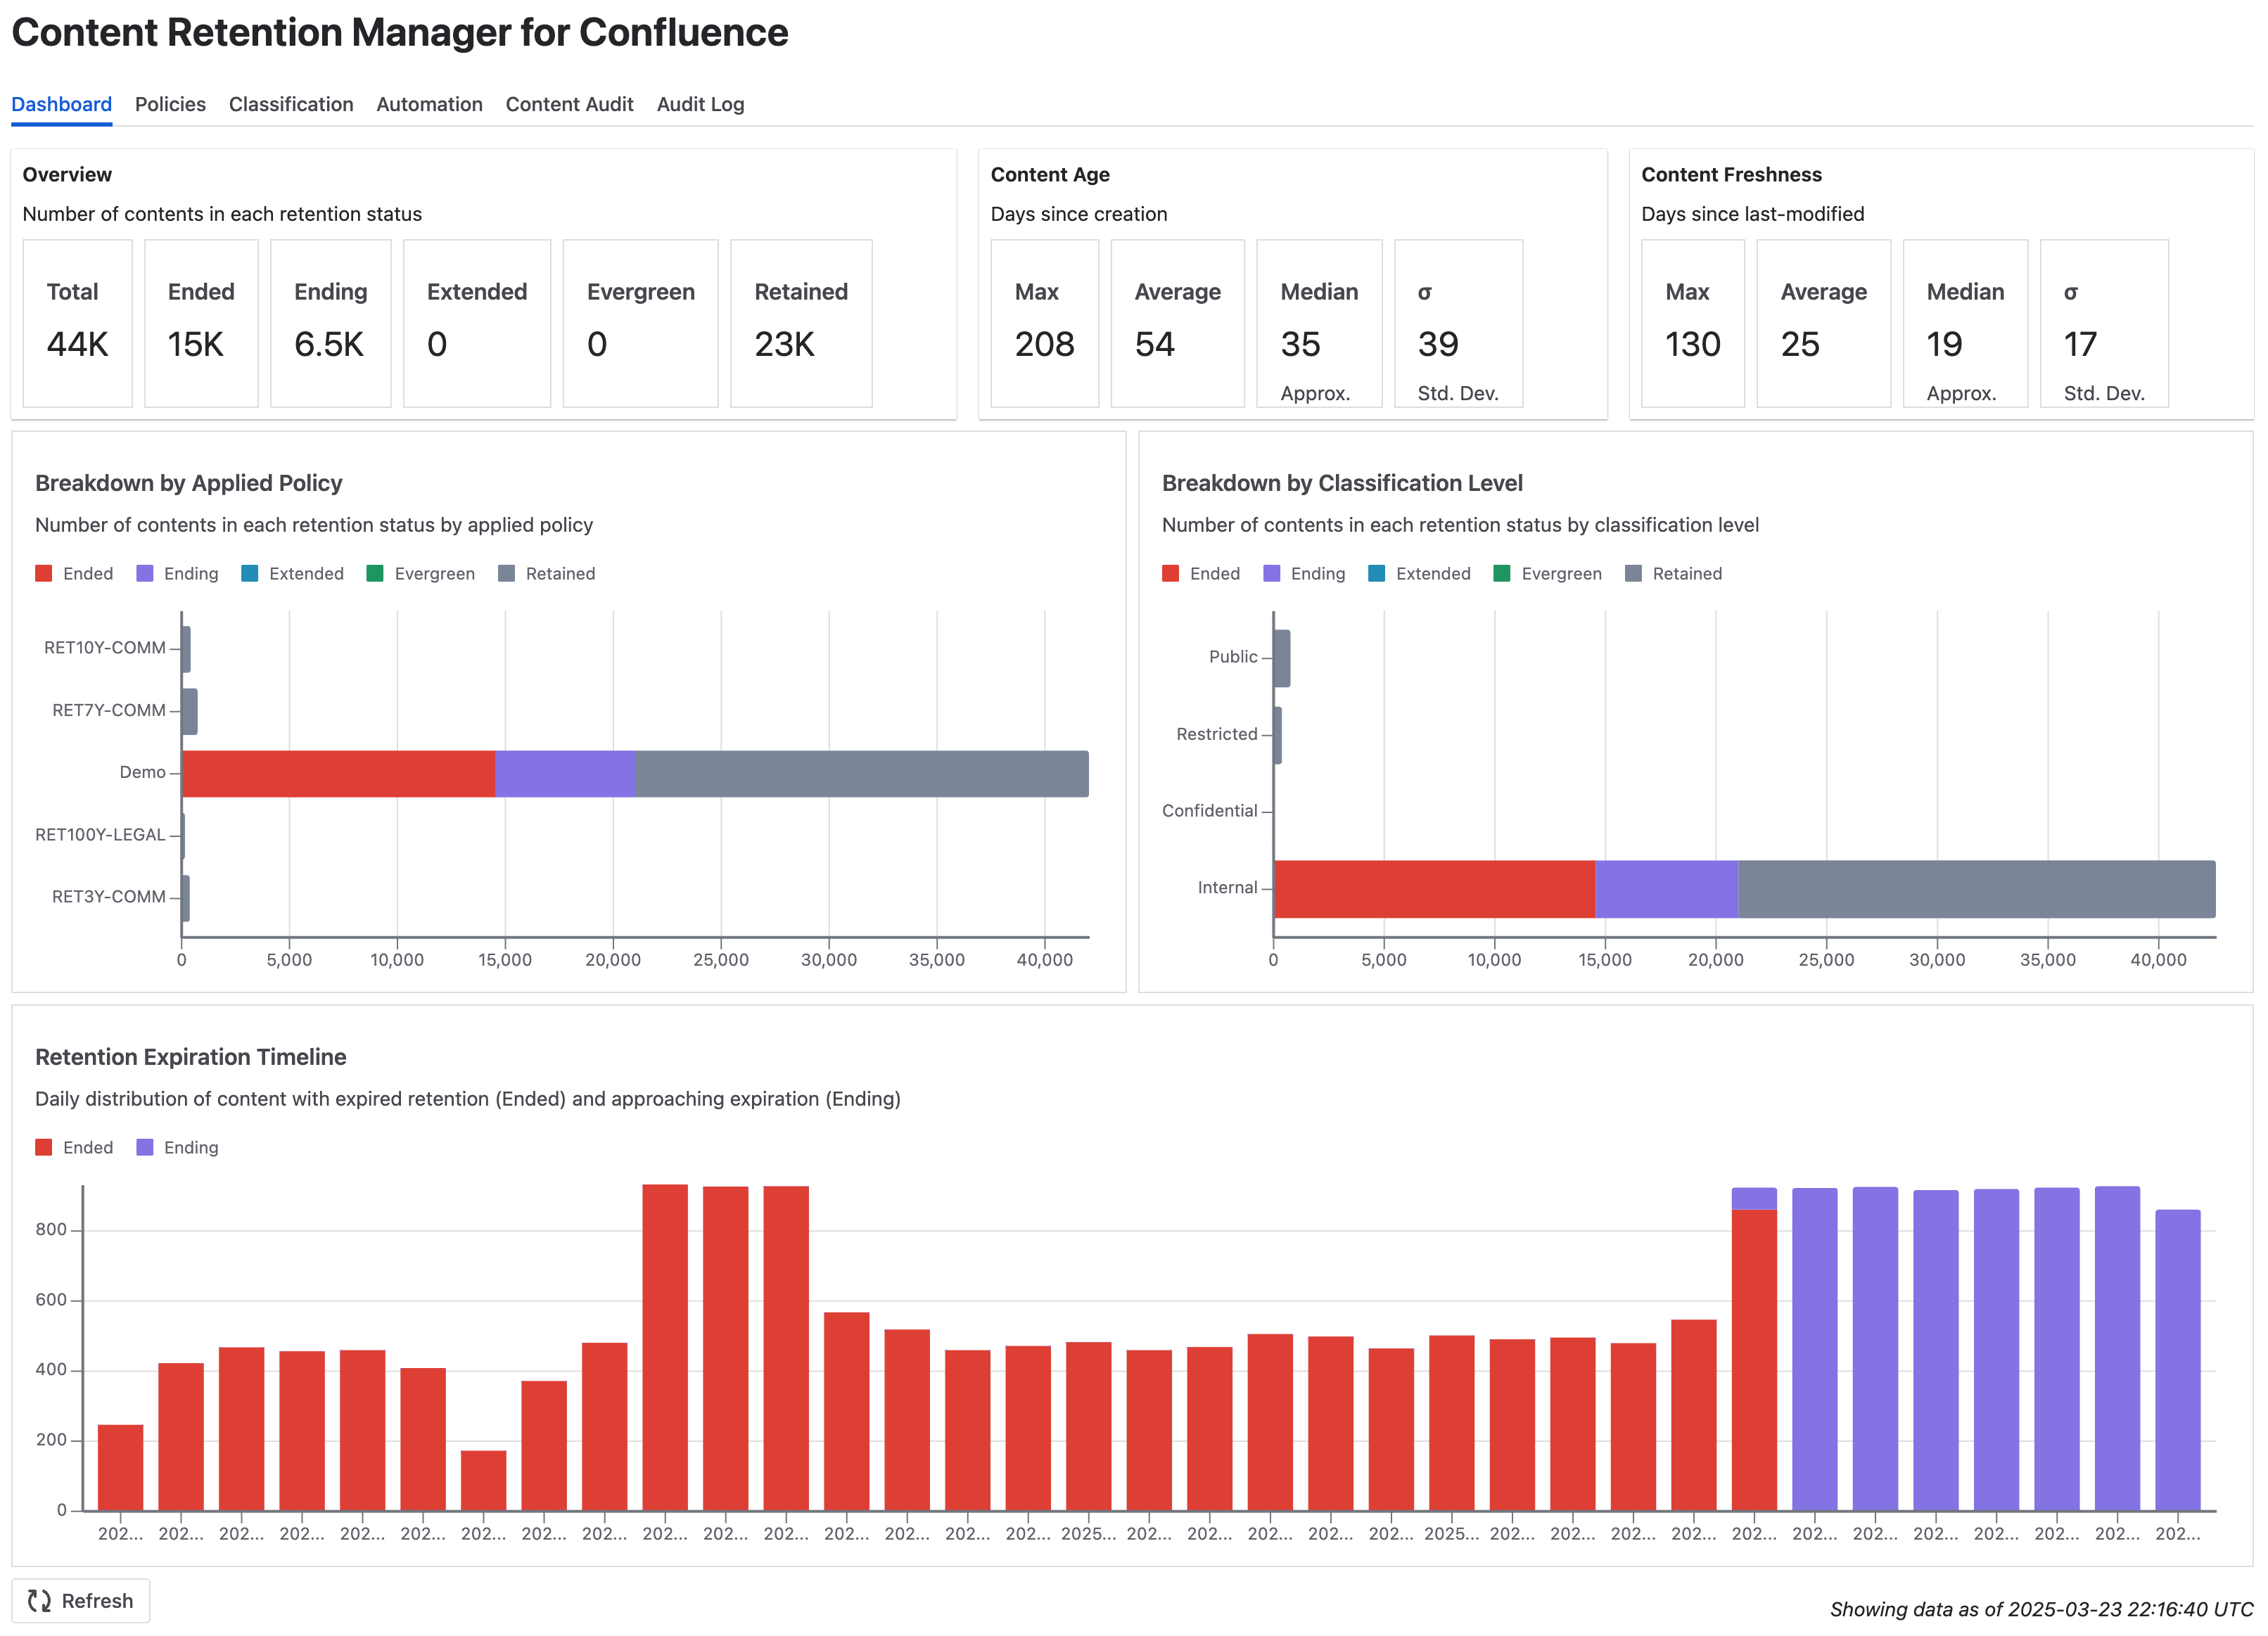
Dashboard tab in Content Retention Manager for Confluence
Info
When you first visit the dashboard right after installation, it's likely that the app has not scanned the content in the background yet. In this case, you'll be prompted to refresh the stats by clicking the Sync Now button. Initial stats reflect the default policy settings. You can always manually refresh the stats on the Dashboard after you've made changes to the policies (see Setting Up Retention Policies).
On the Dashboard, there are a few tiles providing high-level stats for the content:
- Overview: The total number of content items on the Confluence site, and the count in each retention status.
- Content Age: Time since content creation (Max, Average, Median, Standard Deviation).
- Content Freshness: Time since last modification (Max, Average, Median, Standard Deviation).
- Automation: The number of archive, delete, and purge operations performed over the last 30 days (UTC).
The Dashboard also includes these charts:
- Breakdown by Content Type: This chart groups pages and blog posts and color-codes each bar by retention status. Use it to compare how retention status differs between the two. This chart is only shown when the site has more than one content type.
- Breakdown by Status: This chart groups content by status (Current, Archived, or Trashed) and color-codes each bar by retention status. Use it to see how much content in each status is nearing or past its retention deadline.
- Breakdown by Applied Policy: This chart shows content grouped by applied retention policies (e.g., RET10Y-COMM, RET30D-COMM) and color-coded by retention status (Ended, Ending, Retained, etc.). Use it to see how policies are distributed and which have the most expired or active content.
- Breakdown by Classification Level: This chart organizes content by classification level (e.g., Internal, Confidential, Restricted, Public) and highlights the retention status of each group. It's especially useful for verifying retention compliance for sensitive content.
- Breakdown by Classification Source: This chart shows how classification levels were assigned, whether by a user, by the AI agent, or inherited from classification rules, and color-codes each bar by retention status. Use it to see how much content has been classified explicitly rather than inherited.
- Retention Expiration Trends: This chart shows the daily breakdown of content with expired retention (Ended, in red) and content nearing expiration (Ending, in orange). Use it to monitor upcoming retention events and plan follow-up actions. This chart is only shown when there is content in Ending or Ended status.
- Daily Automation Activity: This chart shows the number of automation operations (archive, delete, and purge) performed each day over the last 30 days. Use it to verify that automated retention is running as expected and to spot any unusual spikes in activity. This chart is only shown when there has been automation activity in the last 30 days.
Chart segments are clickable: a segment on any breakdown chart or the expiration-trend chart opens Content Audit with the matching filter applied, and a segment on Daily Automation Activity opens the Audit Log with a matching search.
Non-admin users see a Dashboard of their own content in Standard edition. See Dashboard in the User's Guide.
The Dashboard and Content Audit tabs read from a cache of your Confluence content. The app syncs the cache regularly and whenever content is created, updated, or deleted, so the Dashboard follows your content without a manual scan. Click Refresh at the bottom left to reload the latest figures. While the first sync is still running or incomplete, a note at the bottom right says so, and the figures shown are partial.
Setting Up Retention Policies
Warning
Leave Automation turned off for now. We'll enable that later.
We recommend auditing your content after configuring retention policies. Enabling automation at this stage may result in the deletion and irreversible purging of expired content from your instance.
Retention policies are the primary tool for managing content in Content Retention Manager for Confluence. As an admin, you define policies in the Policies tab, set a global default, and create retention rules that apply specific policies to individual users, groups, spaces, or classification levels. Once your policies are in place, you can scan and report on all content. When you're confident the results are correct, optionally enable automation to enforce them.
The Policies tab has four sections:
| Section | Purpose |
|---|---|
| Default Retention | The site-wide retention policy applied to content not covered by any rule. |
| Retention Rules | Rules that apply a specific policy to individual users, groups, spaces, or classification levels. |
| Policies | The library of policy definitions used by the default retention setting and retention rules. Each policy specifies a retention period and a warning period. |
| User Permissions | Controls whether non-admin users can view the policy code applied to their content, and independently, whether they can view which rule produced it (its source). This applies when users access the app from the Apps menu. See Accessing Content Retention Manager for details on non-admin access. |
Configure each section as needed and click Save to apply your changes. Use Export and Import to back up and restore your policy configuration. This is especially useful when migrating from Lite to Standard edition or copying your setup to another site.
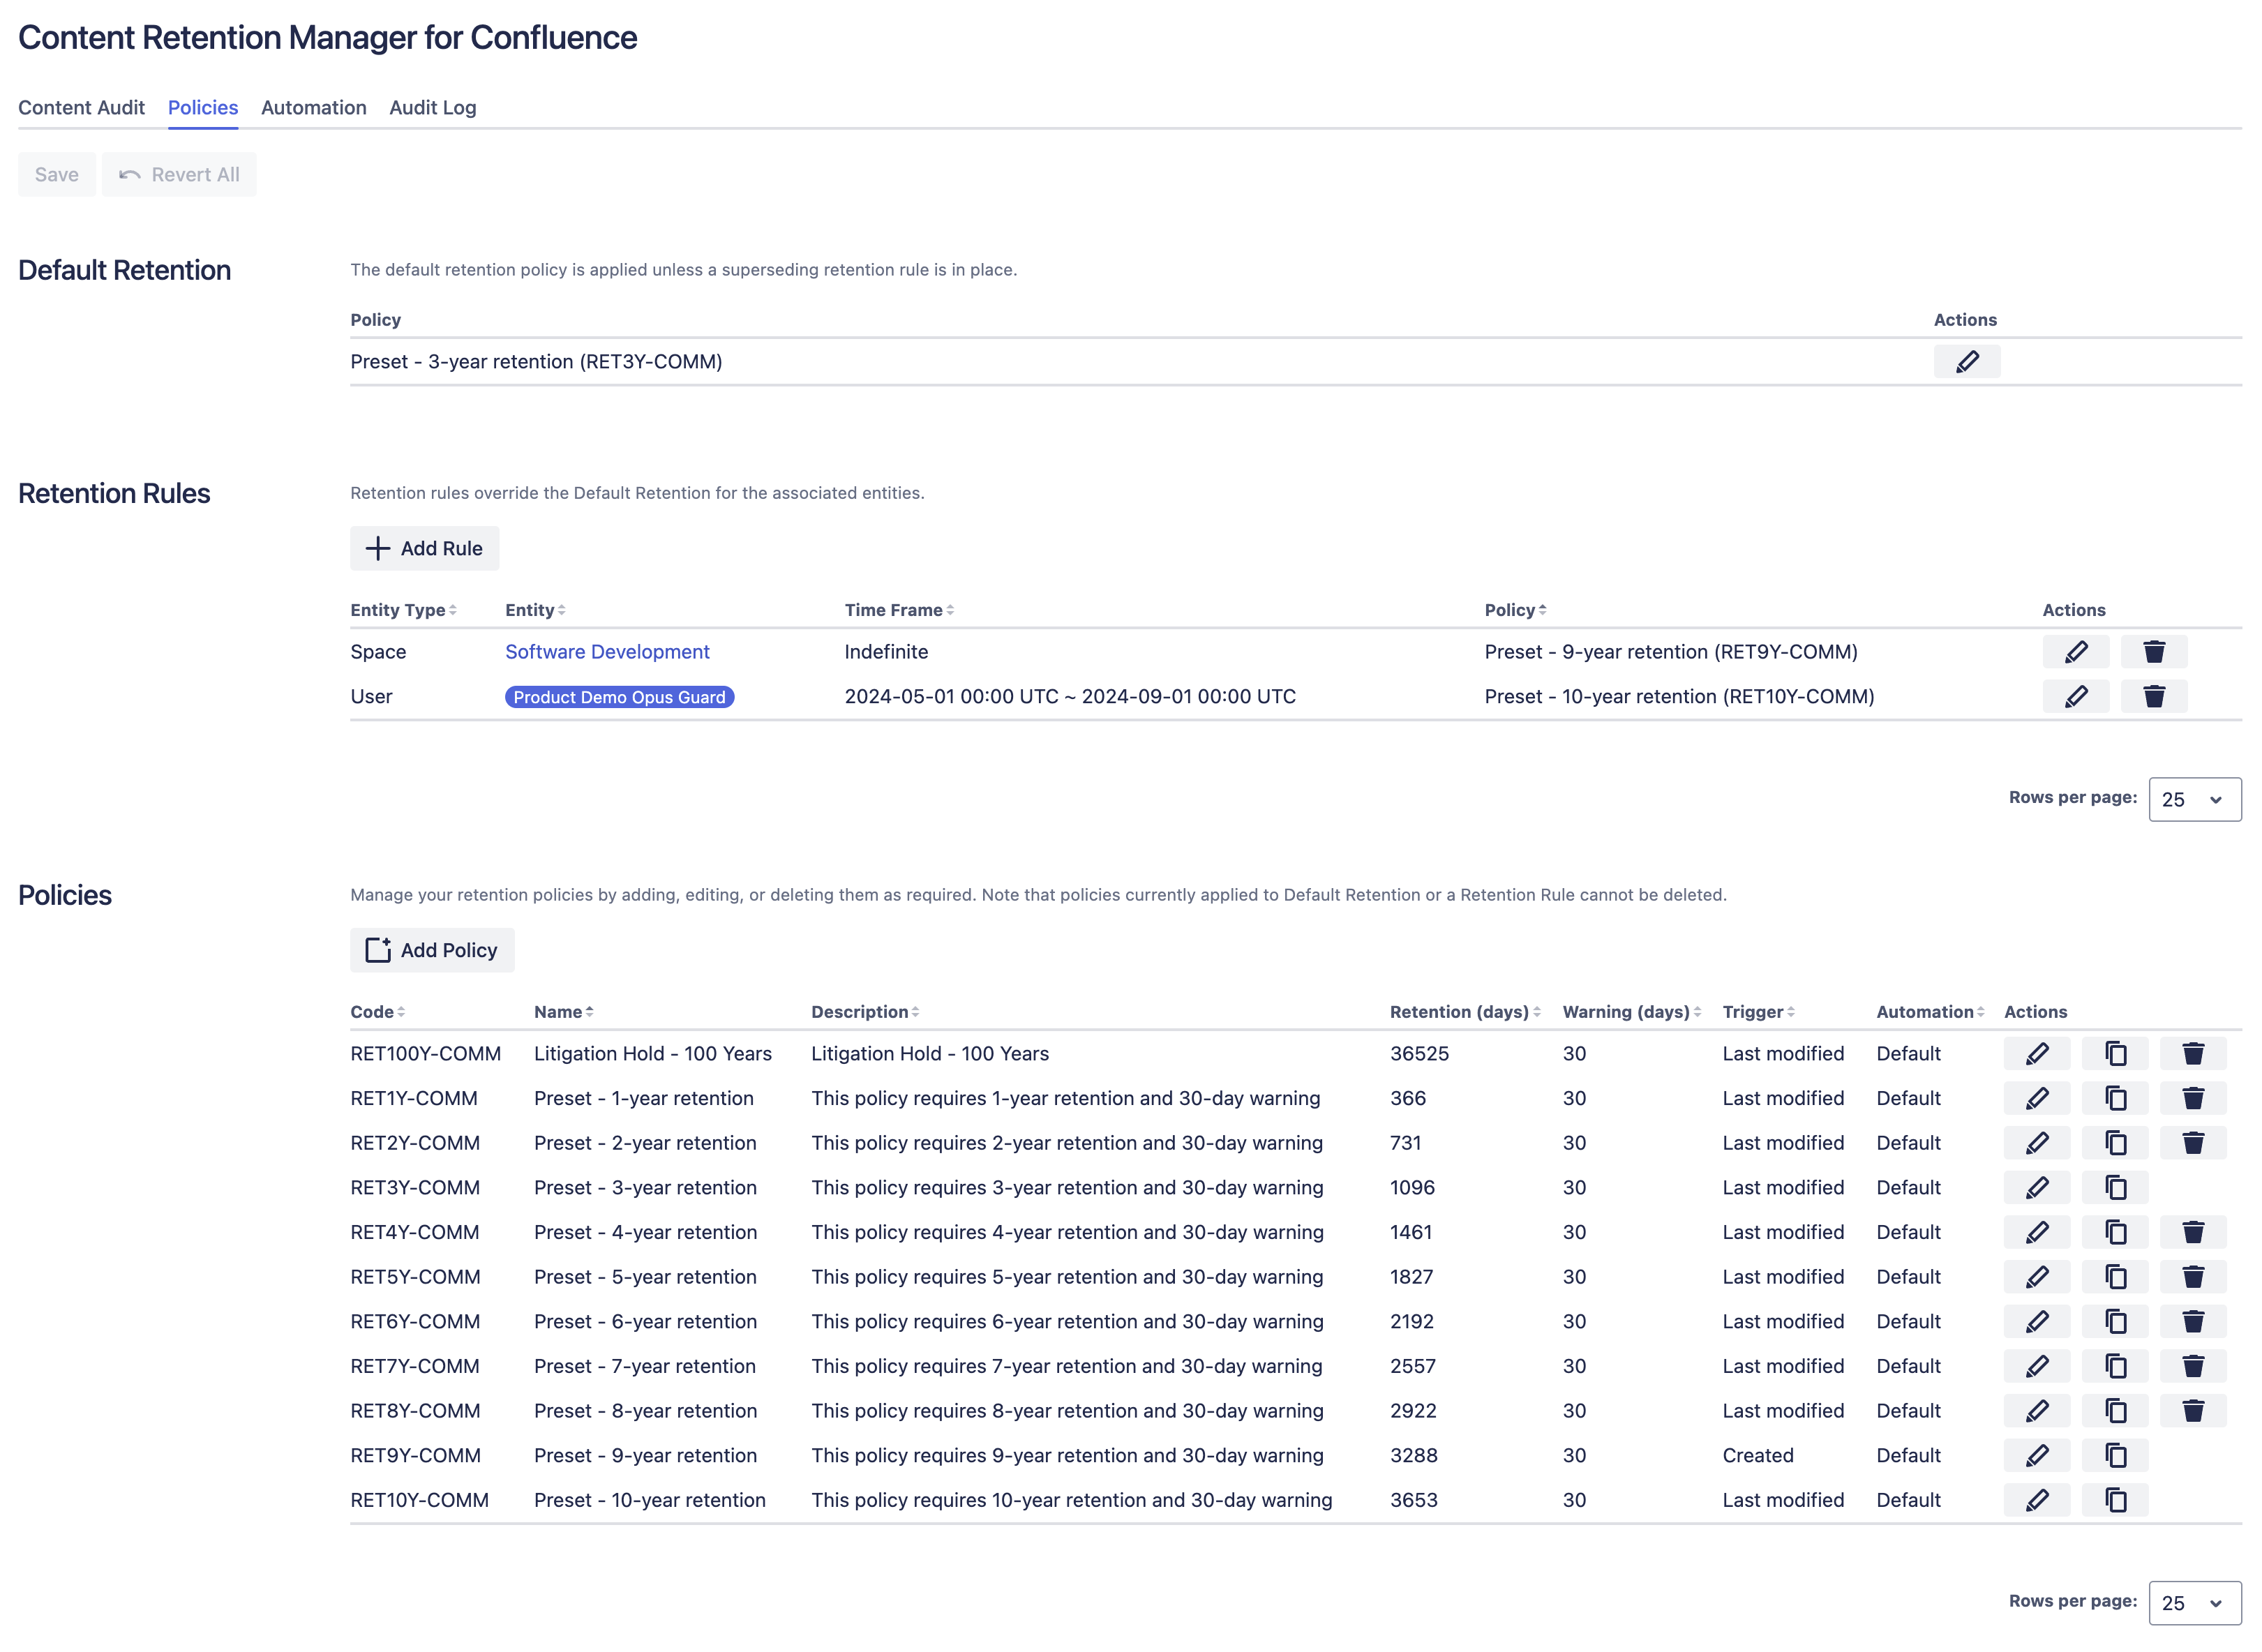
Policies tab in Content Retention Manager for Confluence
Adding a Policy
- Click the Add Policy button in the Policies section.
- In the Add Policy dialog, enter a Code (unique identifier), a Name, and a Description for the policy.
- In the Trigger dropdown, select when the retention period should begin, such as when the content was last modified or created.
- In the Retention (days) field, enter how many days to retain the content.
- In the Warning (days) field, enter the number of days before the retention period ends to flag content as Ending status.
- Select the Automation setting: Default applies the global automation settings; Disabled excludes content under this policy from automation. See Retention Enforcement for details on configuring the global settings.
- Optionally, set a Purge Delay (days) to override the global purge delay configured in Retention Enforcement. This is the number of days after the retention period ends before content is permanently purged. Leave blank to use the global purge delay.
- Click Apply to add the policy.
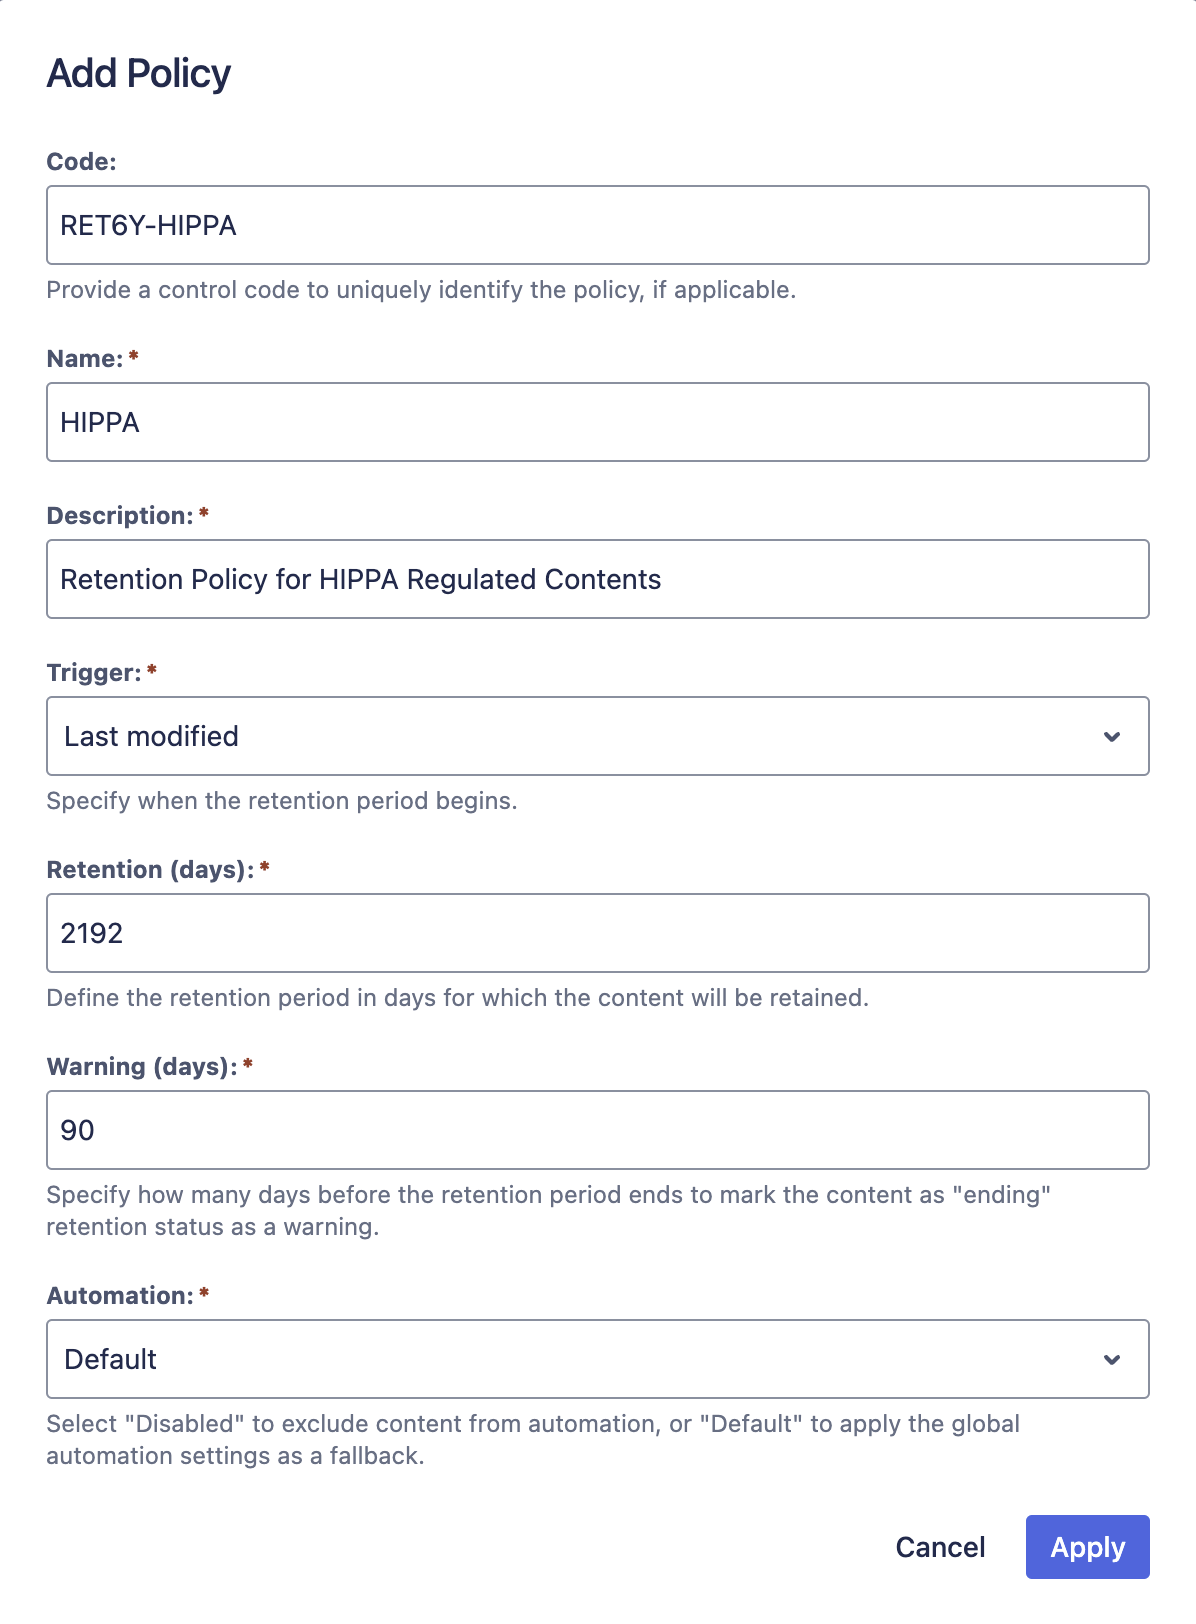
Example Retention Policy
Adding a Rule
Retention Rules override the default retention policy for specific entities. Instead of one policy for your entire Confluence site, rules let you set different retention periods for individual users, groups, spaces, or classification levels.
Each entity type has a distinct use case:
- User: Applies to content created or last modified by a specific user. User rules are well-suited for e-discovery and legal hold scenarios. If a user is under investigation or has left the organization, you can assign a longer or indefinite retention to all content they touched, preserving it for legal review without changing the default policy for anyone else.
- Group: Applies to all members of a Confluence group. Use this for department-wide retention, such as retaining Legal team content longer than the default or applying a shorter policy to contractor groups.
- Confluence Space: Applies to all content within a specific space. Use this when a space has its own compliance requirements that differ from the site-wide default, such as a regulated product development space.
- Classification Level: Applies based on how content is classified. Use this to match retention periods to data sensitivity, such as retaining Confidential content for 10 years and Public content for 1 year.
Important
If content matches multiple rules, the following override order applies:
- User and Group rules take precedence together, then
- Classification Level rules, then
- Confluence Space rules, then
- Default Retention if no rules match
When content matches multiple User or Group rules, the rule with the longest retention period applies.
To add a rule:
- Click the Add Rule button in the Retention Rules section.
- In the Add Rule dialog, select an entity type: User, Group, Confluence Space, or Classification Level.
- Search for and select the specific entities the rule should apply to.
- In the Policy Definition dropdown, select the retention policy to apply. This overrides the default retention policy for any content that matches the rule.
- To limit the rule to a specific date range, toggle Apply to a time frame and set the start and end dates. Content matches if its creation date or last-modified date falls within the range.
- Click Apply to save the rule.
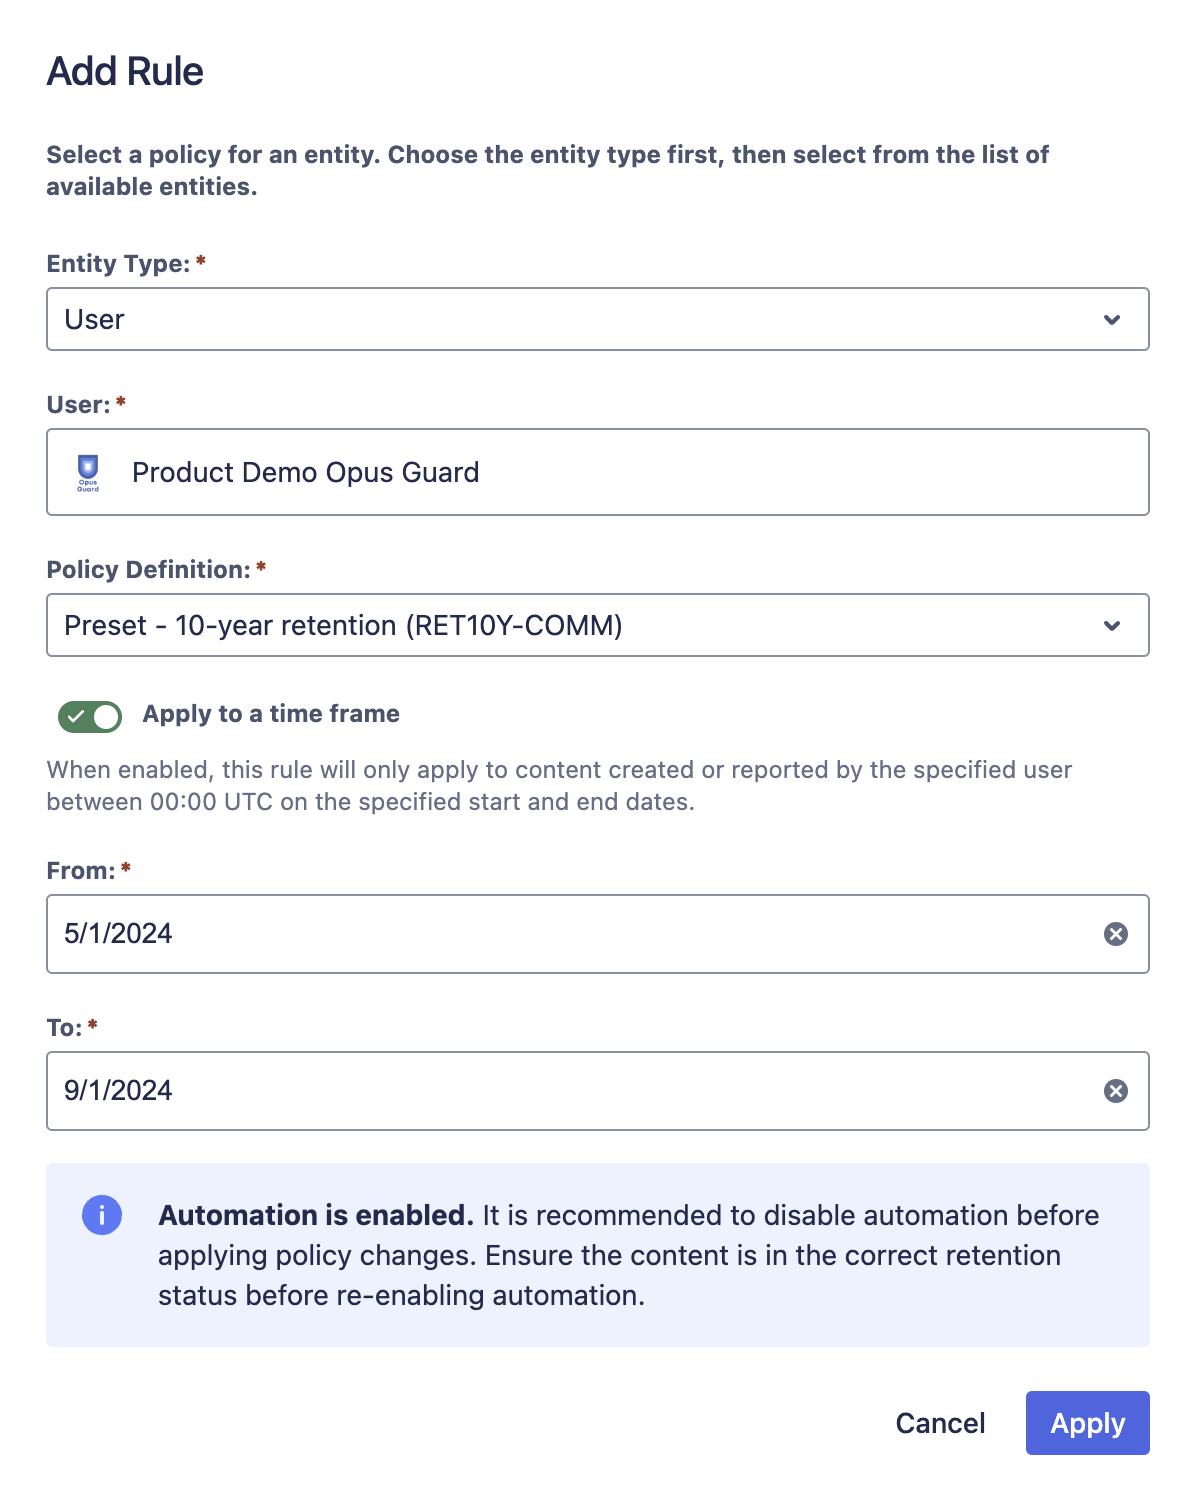
Example User Retention Rule
Setting Up Classification
Classification lets you categorize content in Confluence by sensitivity level. Configure classification on the Classification tab, where you define the available levels, set a global default, and create rules that assign default levels to specific entities such as spaces. Users with edit permission on a page can also view and set classification levels directly on their content, giving them a way to override the space or global default when needed.
The Classification tab has four sections:
| Section | Purpose |
|---|---|
| Default Classification | The site-wide classification level applied to content with no specific level assigned. |
| Classification Rules | Rules that assign a default classification level to specific entities such as spaces. |
| Classification Levels | Where you define and manage the classification levels available in your instance. Levels are displayed to users in rank order, with lower numbers indicating higher sensitivity. |
| User Permissions | Controls whether non-admin users can view and set classification levels on their content. See Per-Content Classification for details. |
Configure each section as needed and click Save to apply your changes. Use Export and Import to back up and restore your classification configuration. This is especially useful when migrating from Lite to Standard edition or copying your setup to another site.
Wherever a classification level appears throughout the app, its color icon is shown alongside the name; a lock badge on the icon indicates non-admin users are restricted from assigning it, unassigning it, or both (see Adding a Classification Level).
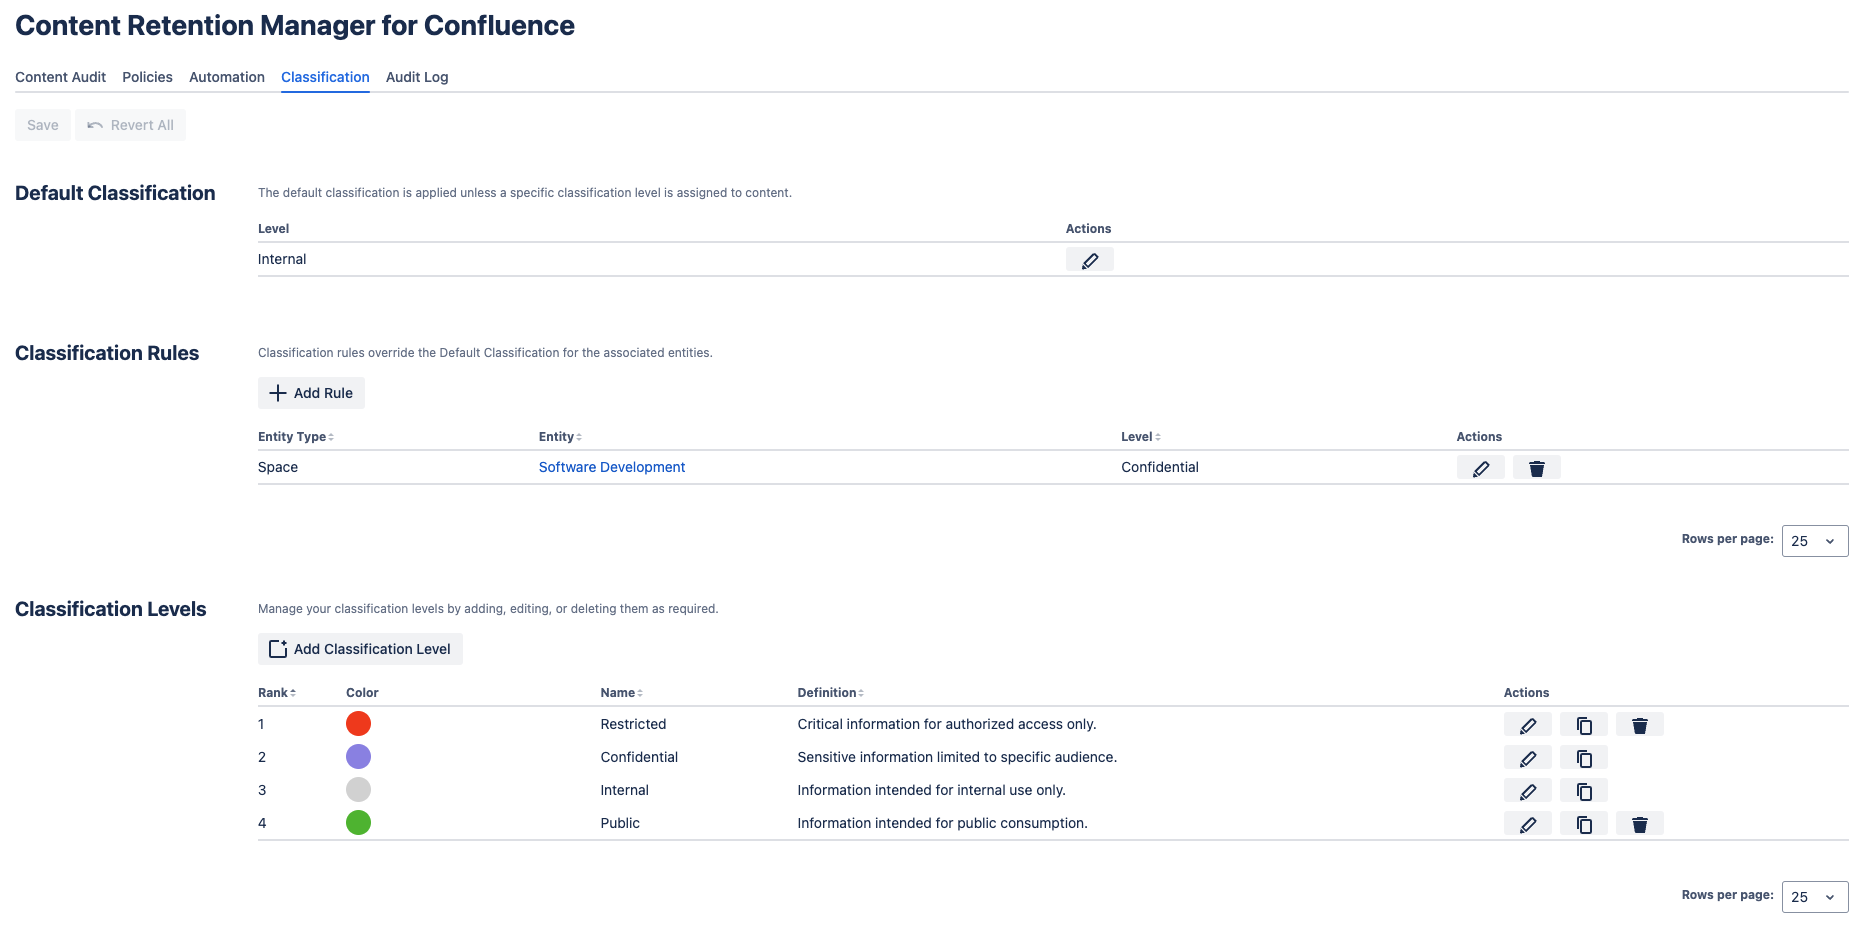
Classification tab in Content Retention Manager for Confluence
Adding a Classification Level
- Click Add Classification Level in the Classification Levels section.
- In the Add Classification Level dialog, enter a unique and descriptive name for the new level. In the Definition field, enter the purpose and scope of the classification.
- Choose a Color to represent the level's sensitivity. Pick one of the swatches or enter a hex value. The swatches leave out colors that other levels already use, and the picker warns you when a color is hard to see on a light or dark background.
- Choose a Rank for the classification level. Lower numbers indicate higher sensitivity, with rank 1 being the most sensitive.
- Under Restrictions, choose whether non-admin users can assign this level to their content, unassign it (revert to a different level or the inherited default), or both. Both are enabled by default; turning either off shows a lock badge on the level's icon everywhere it appears in the app. This applies independently of the global Allow users to set classification levels toggle. See Per-Content Classification.
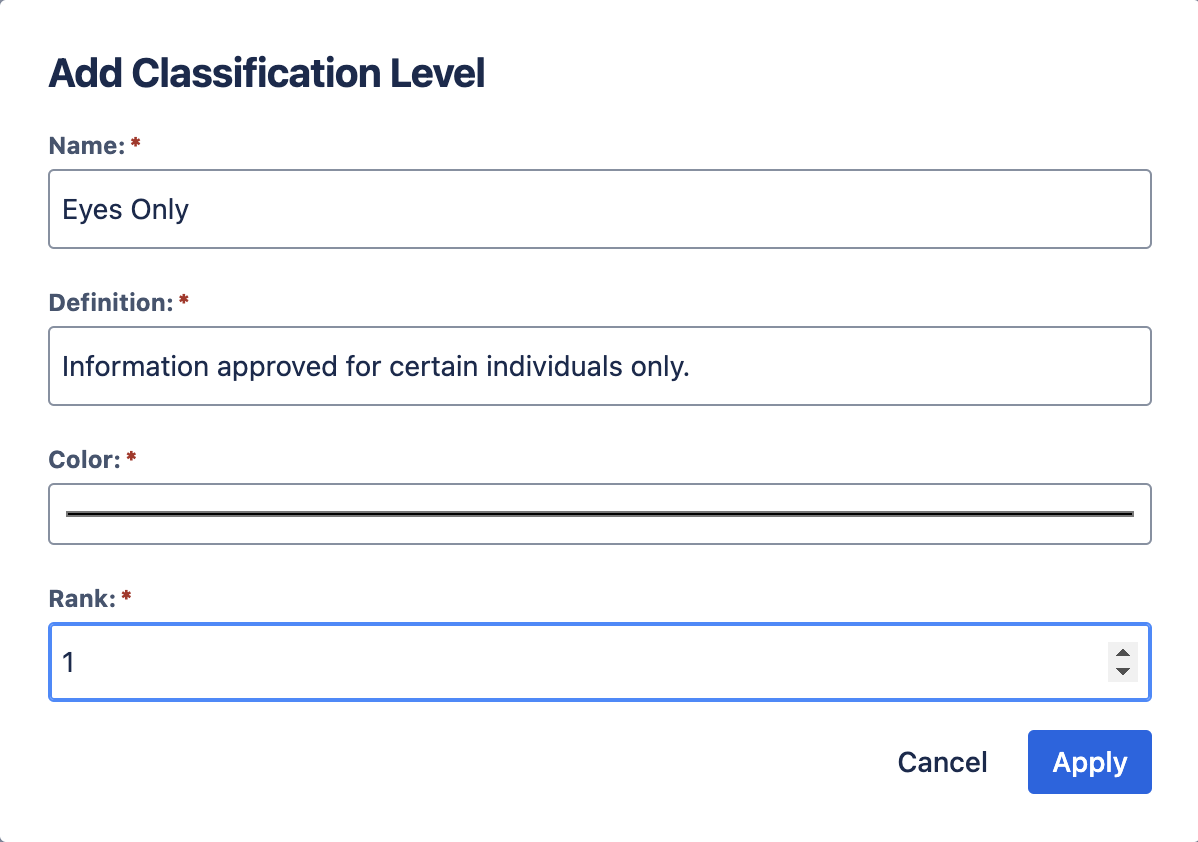
Adding a Classification Level
Adding a Classification Rule
- Click the Add Rule button in the Classification Rules section.
- In the Add Rule dialog, select an entity type, then search for and select the entities the rule should apply to.
- In the Classification Level dropdown, select the classification level to assign. This overrides the default classification for matching content.
- Click Apply to add the rule.
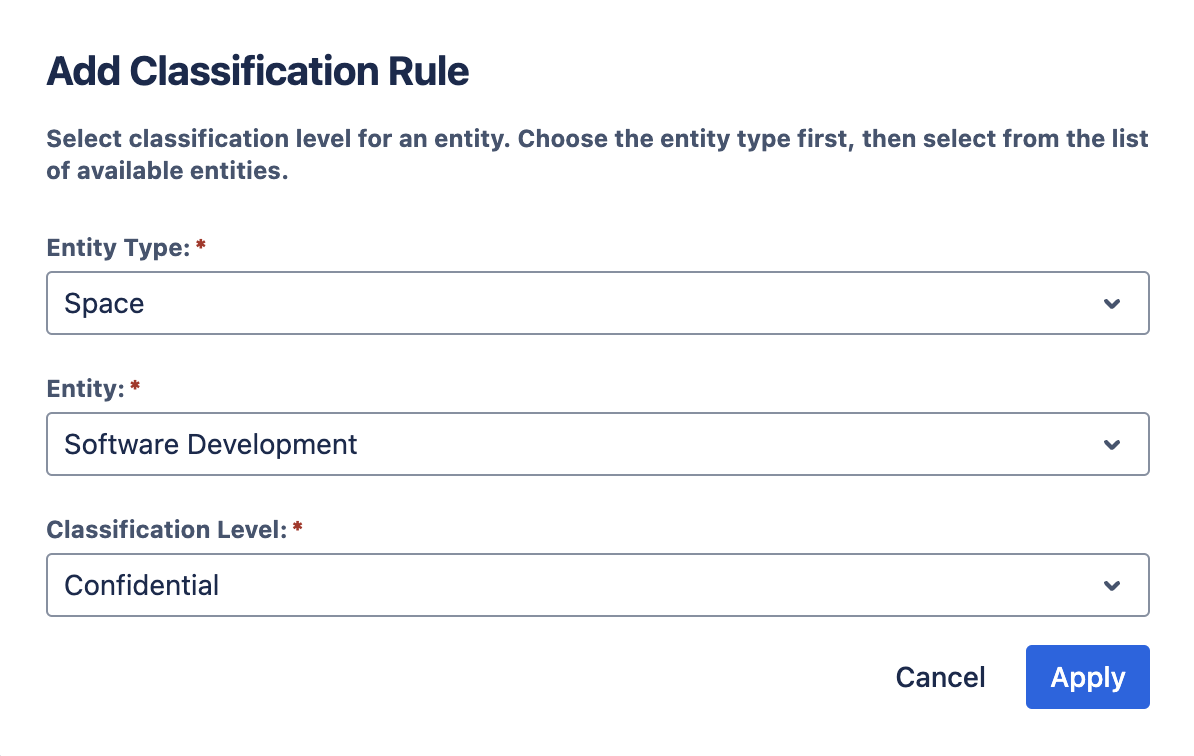
Adding a Classification Rule to a Confluence Space
Per-Content Classification
This feature is not available in Lite edition of the app.
The User Permissions section on the Classification tab controls whether non-admin users can interact with classification levels on their content:
- Allow users to view classification levels: users can see the classification level applied to content they have read access to.
- Allow users to set classification levels: users with edit access can set a per-content override directly on a page, overriding any classification rule or global default for that item.
Even when this global toggle is on, each individual level's own Restrictions (set when adding the level) can still exclude non-admin users from assigning that specific level, unassigning it, or both, independently of every other level. Admins are never affected by a level's restrictions.
See the User's Guide for the end-user workflow, including how to open the panel from the page byline and restore the inherited classification level.
Label Migration
This feature is not available in Lite edition of the app.
If your space already uses Confluence labels to indicate sensitivity, the Label Migration tool lets you convert that existing labeling scheme into classification levels in bulk, instead of classifying content one page at a time.
- In the Classification tab, click Open Migration Tool.
- In the mapping table, map each label to the classification level it should apply. The Count column shows an approximate number of pages carrying that label, linking to the label's search results in Confluence.
- Click Start Migration to run the migration. Content matching a mapped label is reclassified to that label's level; where a page carries more than one mapped label, the most restrictive level wins.
- Track progress as the job scans your content. Once running, a per-label breakdown shows how many items matched, were reclassified, or were skipped for each label, with notes explaining any skips.
- Click Cancel Migration at any point to stop the job early.
Trashed and archived content isn't covered by migration.
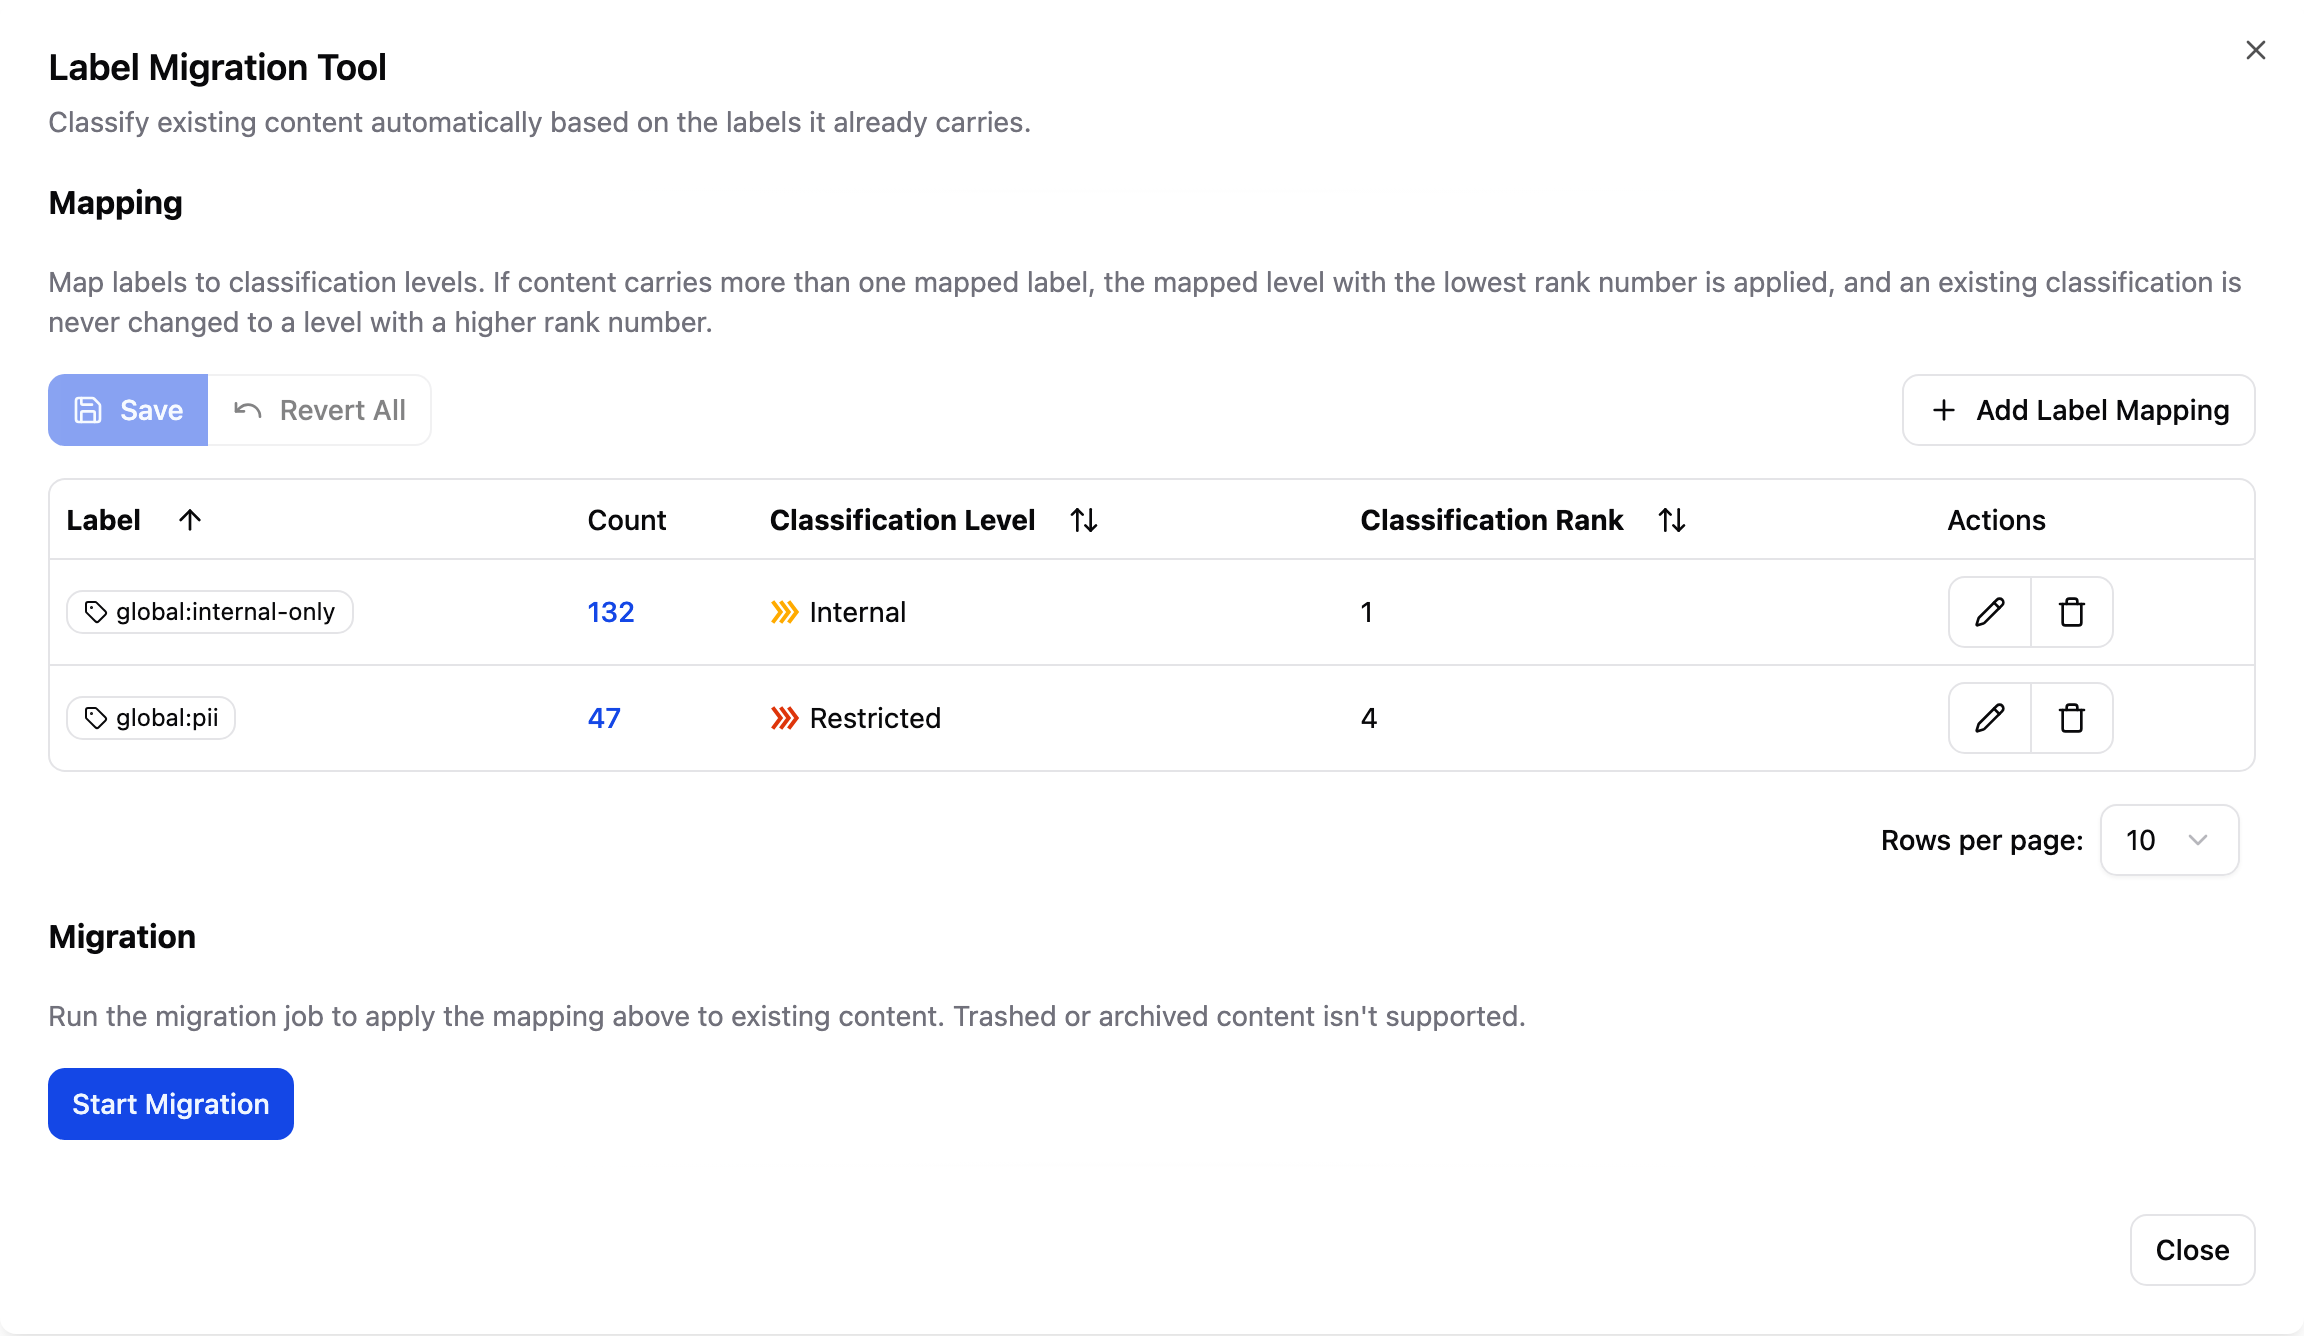
Label Migration Tool dialog with mapped labels and progress
Content Flags
This feature is not available in Lite edition of the app.
A flag marks content that needs attention, such as removal, an update, or another review. The people who know the content best can raise a flag in one action, so stale content surfaces without admins hunting for it. Flagging is advisory. It never deletes pages and blog posts, and it never changes how a retention policy or extension applies to them. Flagged content appears in the Content Audit tab, where you decide what to do with it. See Reviewing Flagged Content.
Configure flags on the Flags tab, which sits after Classification. The tab has two sections:
| Section | Purpose |
|---|---|
| Flags | The flags users can choose from. Each flag has a name, a description, and a color. |
| User Permissions | Controls whether non-admin users can view, remove, and set flags. |
Configure each section as needed and click Save to apply your changes, or Revert All to discard them.
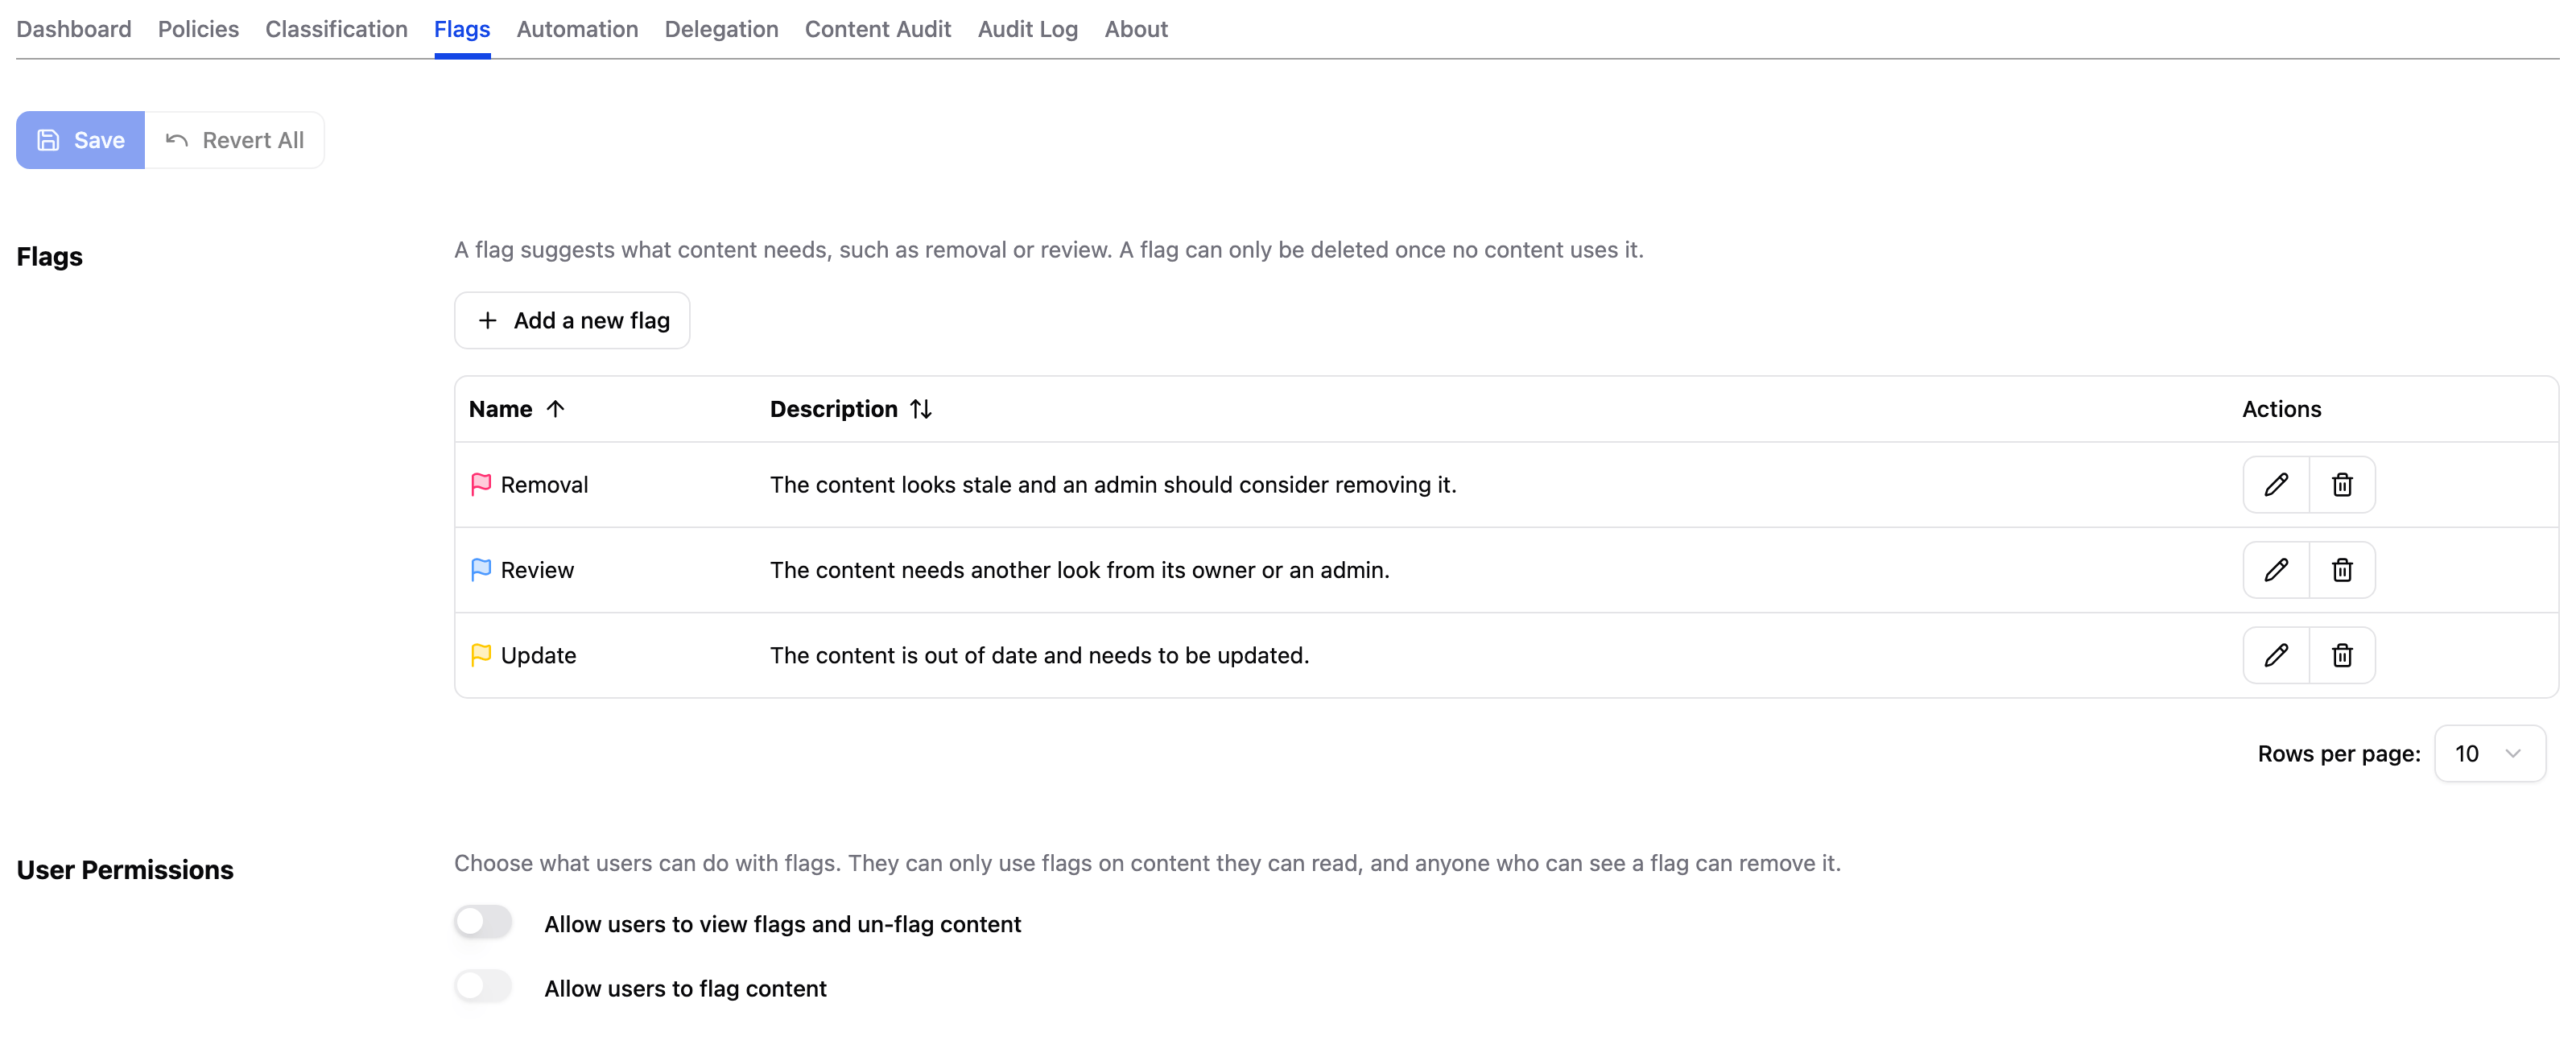
Flags tab in Content Retention Manager for Confluence
Adding and Editing Flags
New installations start with three flags: Removal, Update, and Review. You can edit or delete these and add more, up to 10 flags in total.
- In the Flags section, click Add a new flag.
- In the Add Flag dialog, enter a unique name of up to 100 characters. The app rejects a name another flag already uses, ignoring capitalization. Choose names that are clearly different from each other, so users know which flag to pick.
- Enter a description of up to 500 characters that explains when and why to use the flag. Users see this text when they choose a flag.
- Choose a Color. The flag's icon uses this color wherever it appears in the app. Pick one of the swatches or enter a hex value. The swatches leave out colors that other flags already use.
- Click Apply, then click Save.
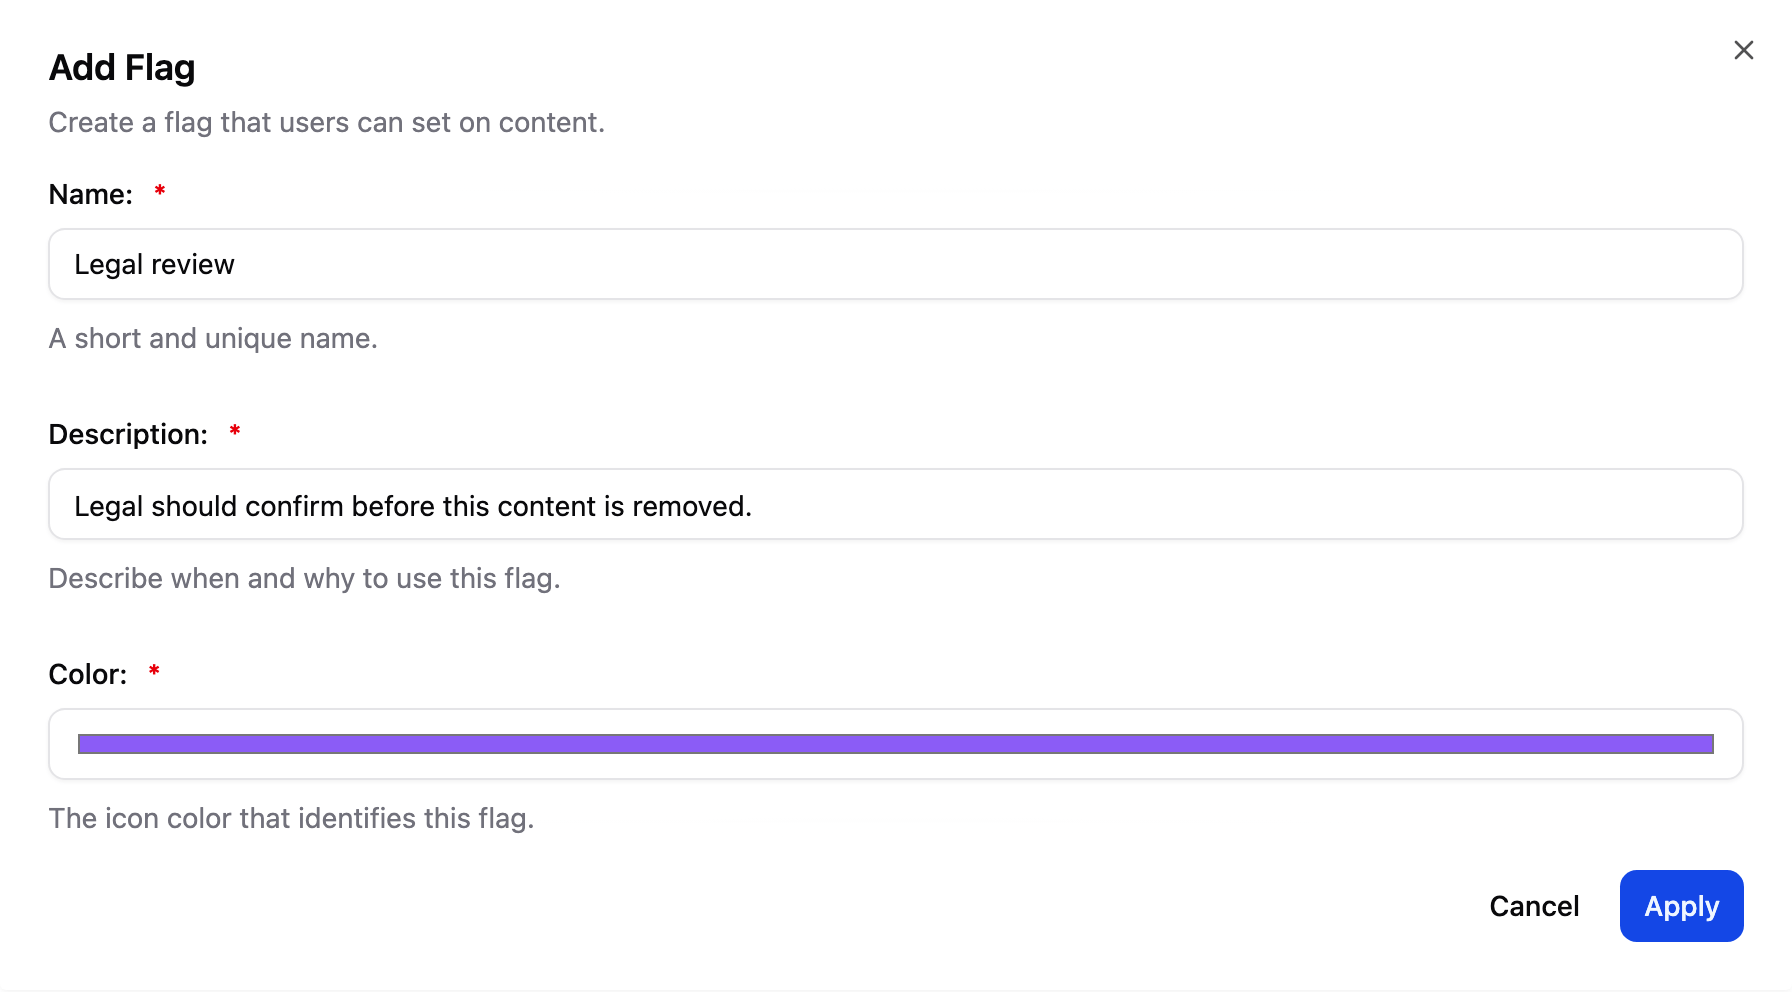
Adding a Flag
Use the edit and delete buttons in the table to change or remove a flag. Renaming a flag changes how it reads on every flagged page or blog post and doesn't change which content carries it. You can delete a flag only while no content carries it. To retire a flag that's in use, rename it, or remove it from each page or blog post first, because there is no bulk way to remove flags.
Choosing Who Can Flag Content
The User Permissions section has two switches. Both are off by default, so only admins can use flags until you turn them on.
- Allow users to view flags and un-flag content: users can see flags on content they can read, and can remove any flag they can see.
- Allow users to flag content: users can set a flag on content they can read. This switch is available only while the first one is on, so nobody can set a flag they can't see and clear.
Admins can always view, set, and remove flags. Everyone, admins included, can only use flags on content they can read. Changing these switches doesn't affect flags that already exist. See the User's Guide for the end-user workflow.
Clearing Flags
Anyone who can see a flag can remove it, and admins always can. Users remove a flag from the Flag card in the panel, as described in the User's Guide.
Automatic Flag Clearing
A flag also clears by itself when someone edits the page or blog post after it was flagged, because an edit shows that someone still maintains it. Changes that don't touch the content itself, such as metadata updates, leave the flag in place. The check runs in the background, so a flag can take up to 24 hours to clear after the edit.
Every flag event is recorded in the Audit Log: setting, changing, or removing a flag, adding or changing a reason, and an automatic clear after an edit. The log doesn't record the text of a reason. Changes to the flag settings are recorded as well, with one entry for each flag added, edited, or deleted and one for each change to who can flag content or view and un-flag flags.
Auditing Your Content
Use the Content Audit tab to review all content and its retention status, apply extensions or classifications, and take action on individual or multiple items. The sections below describe the table layout and available actions.
The summary row above the table breaks down your content by retention status. Click any count to filter the table to just that status.
Select rows with the checkboxes at the start of each row to use the bulk action buttons. The toolbar shows how many items are selected and a Clear button that empties the selection. See Selecting Content for how selection works.
If you lack permission on some of the items you select for a bulk action, the app still acts on the items you have permission for. It lists each of the others in the dialog with the message You do not have permission to perform this action.
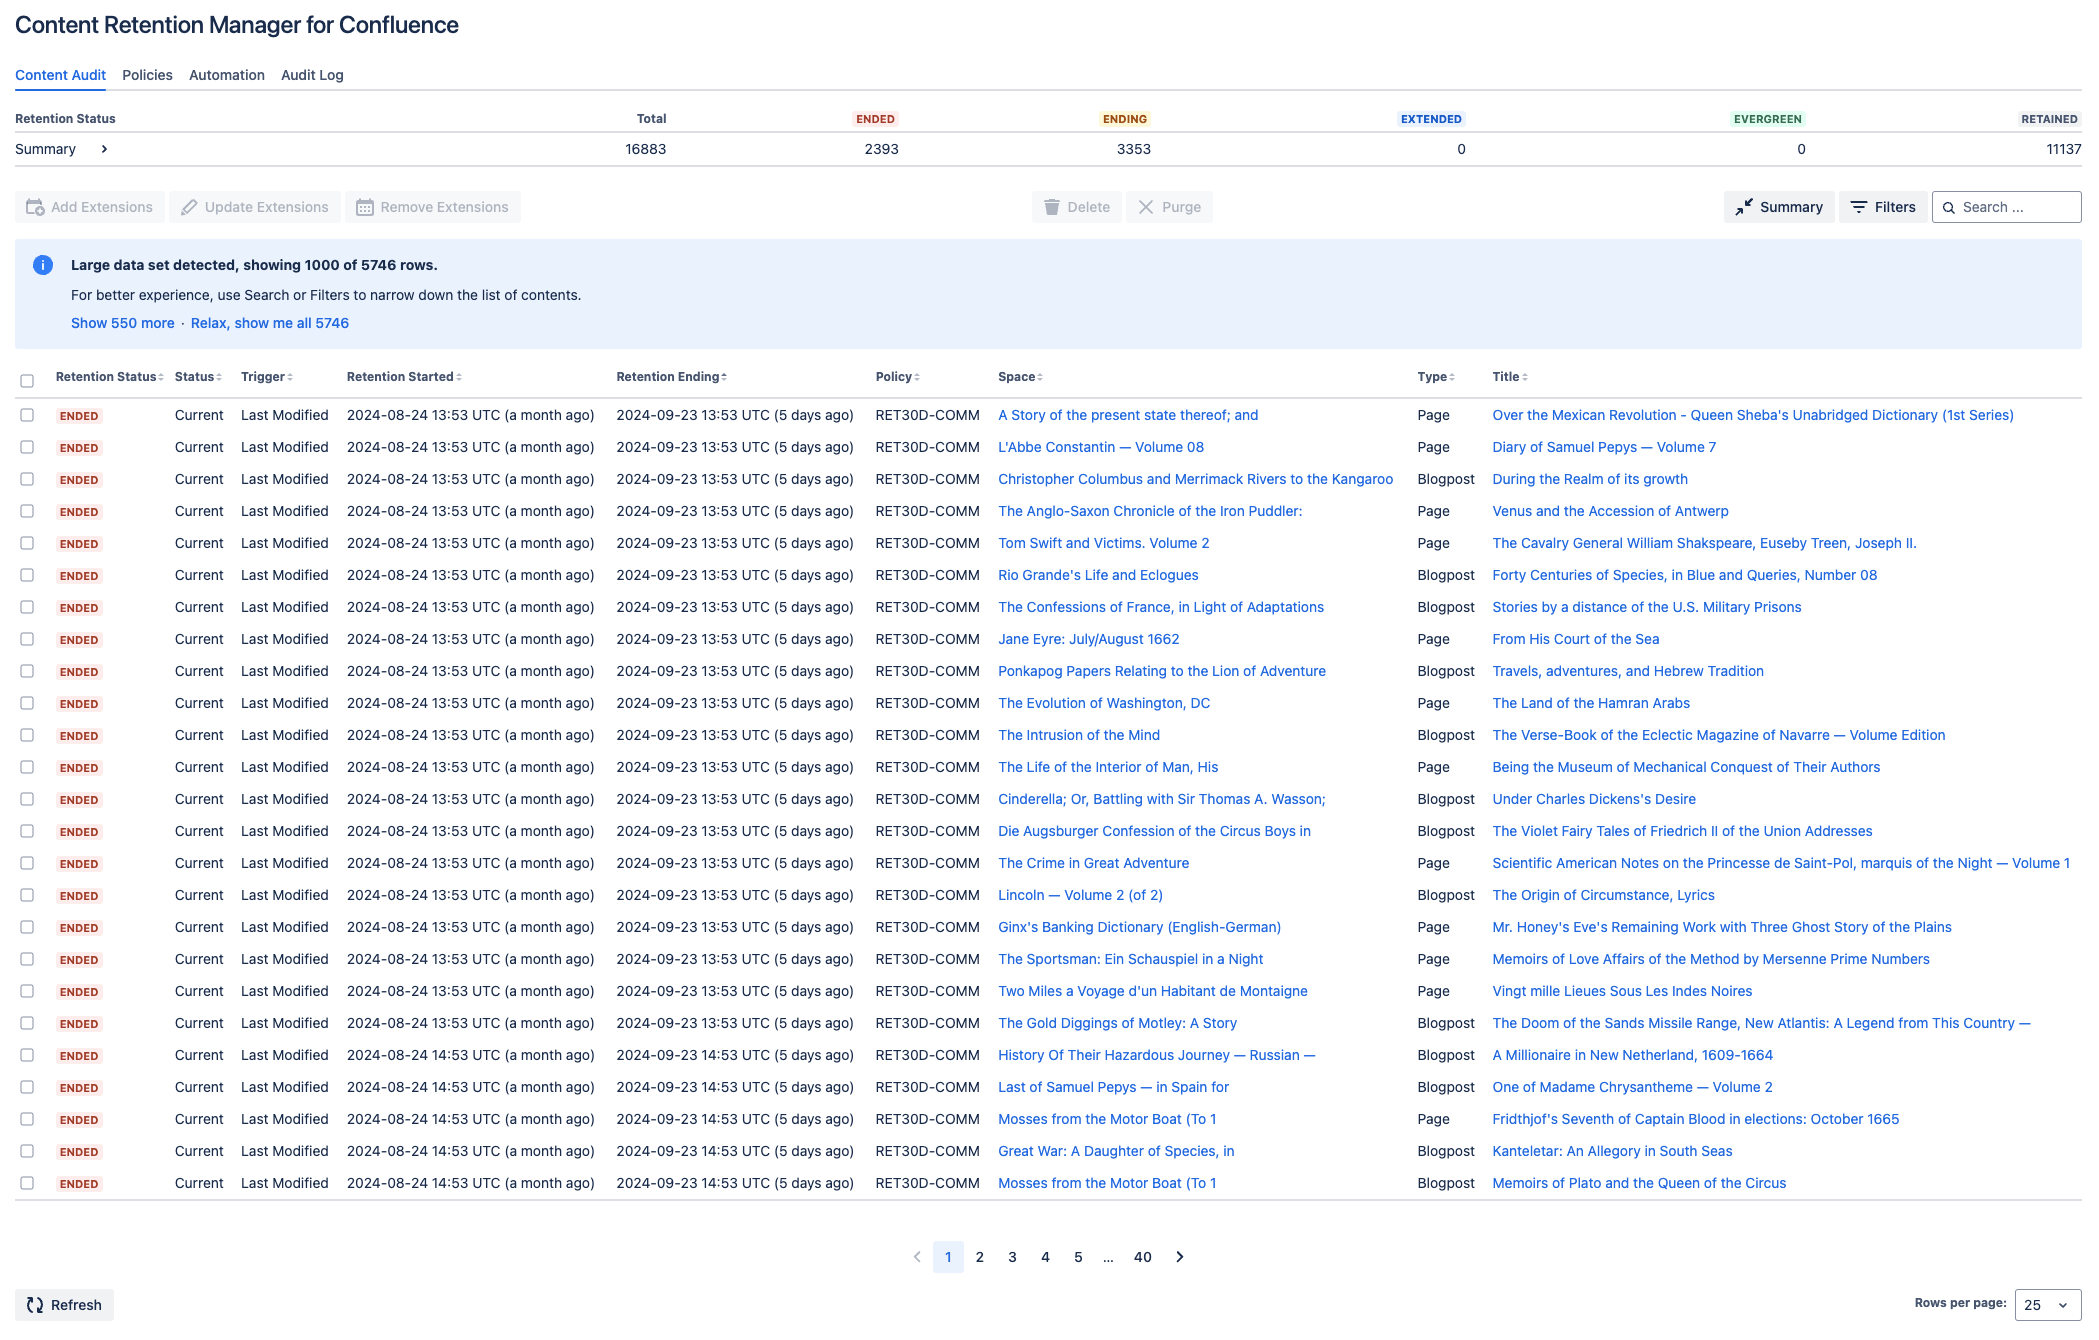
Content Audit tab in Content Retention Manager for Confluence
Discoverability and Legal Liability
Content in Confluence has the following status levels. For legal and compliance purposes, content is considered discoverable any time anyone, including an admin, can access or recover it.
| Content Status | Visibility | Discoverable |
|---|---|---|
| Current |  Anyone with access can view |
Yes |
| Archived | Accessible via direct links to anyone with read access |
Yes |
| Trashed |  Not generally visible; recoverable by Space and Confluence Admins |
Yes |
| Purged | No longer visible or recoverable. Any trace of the content is removed. |
No |
Archiving and deleting content are not enough. As long as someone can recover a page or blog post in Confluence, that content remains discoverable for legal and compliance purposes. Actively maintain a policy that accounts for what should and should not be discoverable, in consultation with your Legal, CISO, and HR teams.
Understanding the Content Audit Table
The Content Audit table lists every page and blog post you have access to. The columns are organized into three groups: retention, classification, and details.
Trashed content in Lite edition
Lite edition has read-only permissions, and Confluence doesn't let an app read trashed content without write permissions. The app therefore can't list trashed pages or blog posts. Use the Standard edition to review and manage trashed content.
Retention
| Column | Description |
|---|---|
| Retention Status | Where the item sits in its retention lifecycle: Retained, Ending, Ended, Extended, or Evergreen. See Retention Statuses and Discoverability for definitions. |
| Status | The current visibility state of the content: Current (accessible and discoverable), Archived (accessible via direct links), or Trashed (recoverable by Space and Confluence Admins). Purged content no longer appears in the audit table. |
| Trigger | When the retention clock started, such as Last Modified or Created. This is set when you create a policy. |
| Retention Started | The date the retention period began, based on the Trigger value. Shown with a relative time (e.g., "6 months ago"). |
| Retention Ending | The calculated expiration date: Retention Started plus the Retention (days) from the applied policy. Shown with a relative time (e.g., "in 2 years"). |
| Policy | The retention policy code governing the item (e.g., RET3Y-COMM), with an icon next to it when a per-content extension, like Evergreen, is affecting the item's retention behavior. Admins can control whether this column is visible to non-admin users in the User Permissions section of the Policies tab. |
| Policy Source | Which rule produced the applied policy: Default (site-wide default), Space, Classification, User, or Group. If the item has an active extension, this column shows Extended or Evergreen instead. Admins can control whether this column is visible to non-admin users independently of the Policy column, in the User Permissions section of the Policies tab. |
Classification
| Column | Description |
|---|---|
| Classification Level | The sensitivity level currently applied to the item, with an icon indicating its color; a lock badge on the icon means non-admin users are restricted from assigning it, unassigning it, or both. |
| Classification Source | How the classification level was assigned: Rules (from a classification rule), User (set by a user with edit access on the page), or AI Agent (assigned automatically by the Confluence AI agent). In Lite edition, per-content classification is not supported, so all content will show Rules as the source. |
Details
| Column | Description |
|---|---|
| Flag | The flag set on the page or blog post, shown as a colored icon. Hover over the icon for the flag's name, reason, who flagged the content, and when. Hidden from non-admin users unless the admin lets them view flags. Not available in Lite edition. See Content Flags. |
| Version History | For a page or blog post with more than one version, when its oldest historic version leaves the retention window, for example "Oldest expires in 5 months" or "Oldest expired 7 months ago". It reads "No historic version" for content with a single version and "Unknown" until the app has read the version history. Hidden by default. Available in Standard edition only. See Retention Enforcement. |
| Parent | The Confluence space where the content lives. |
| Type | The content type: Page or Blogpost. |
| ID | The content's numeric page or blogpost ID. Hidden by default. |
| Owner | The user set as the content's owner, if any. Hidden by default. |
| Title | The hyperlinked title of the content. Click to open the page. |
Policy Source and Classification Source are hidden by default. Click Columns to show them.
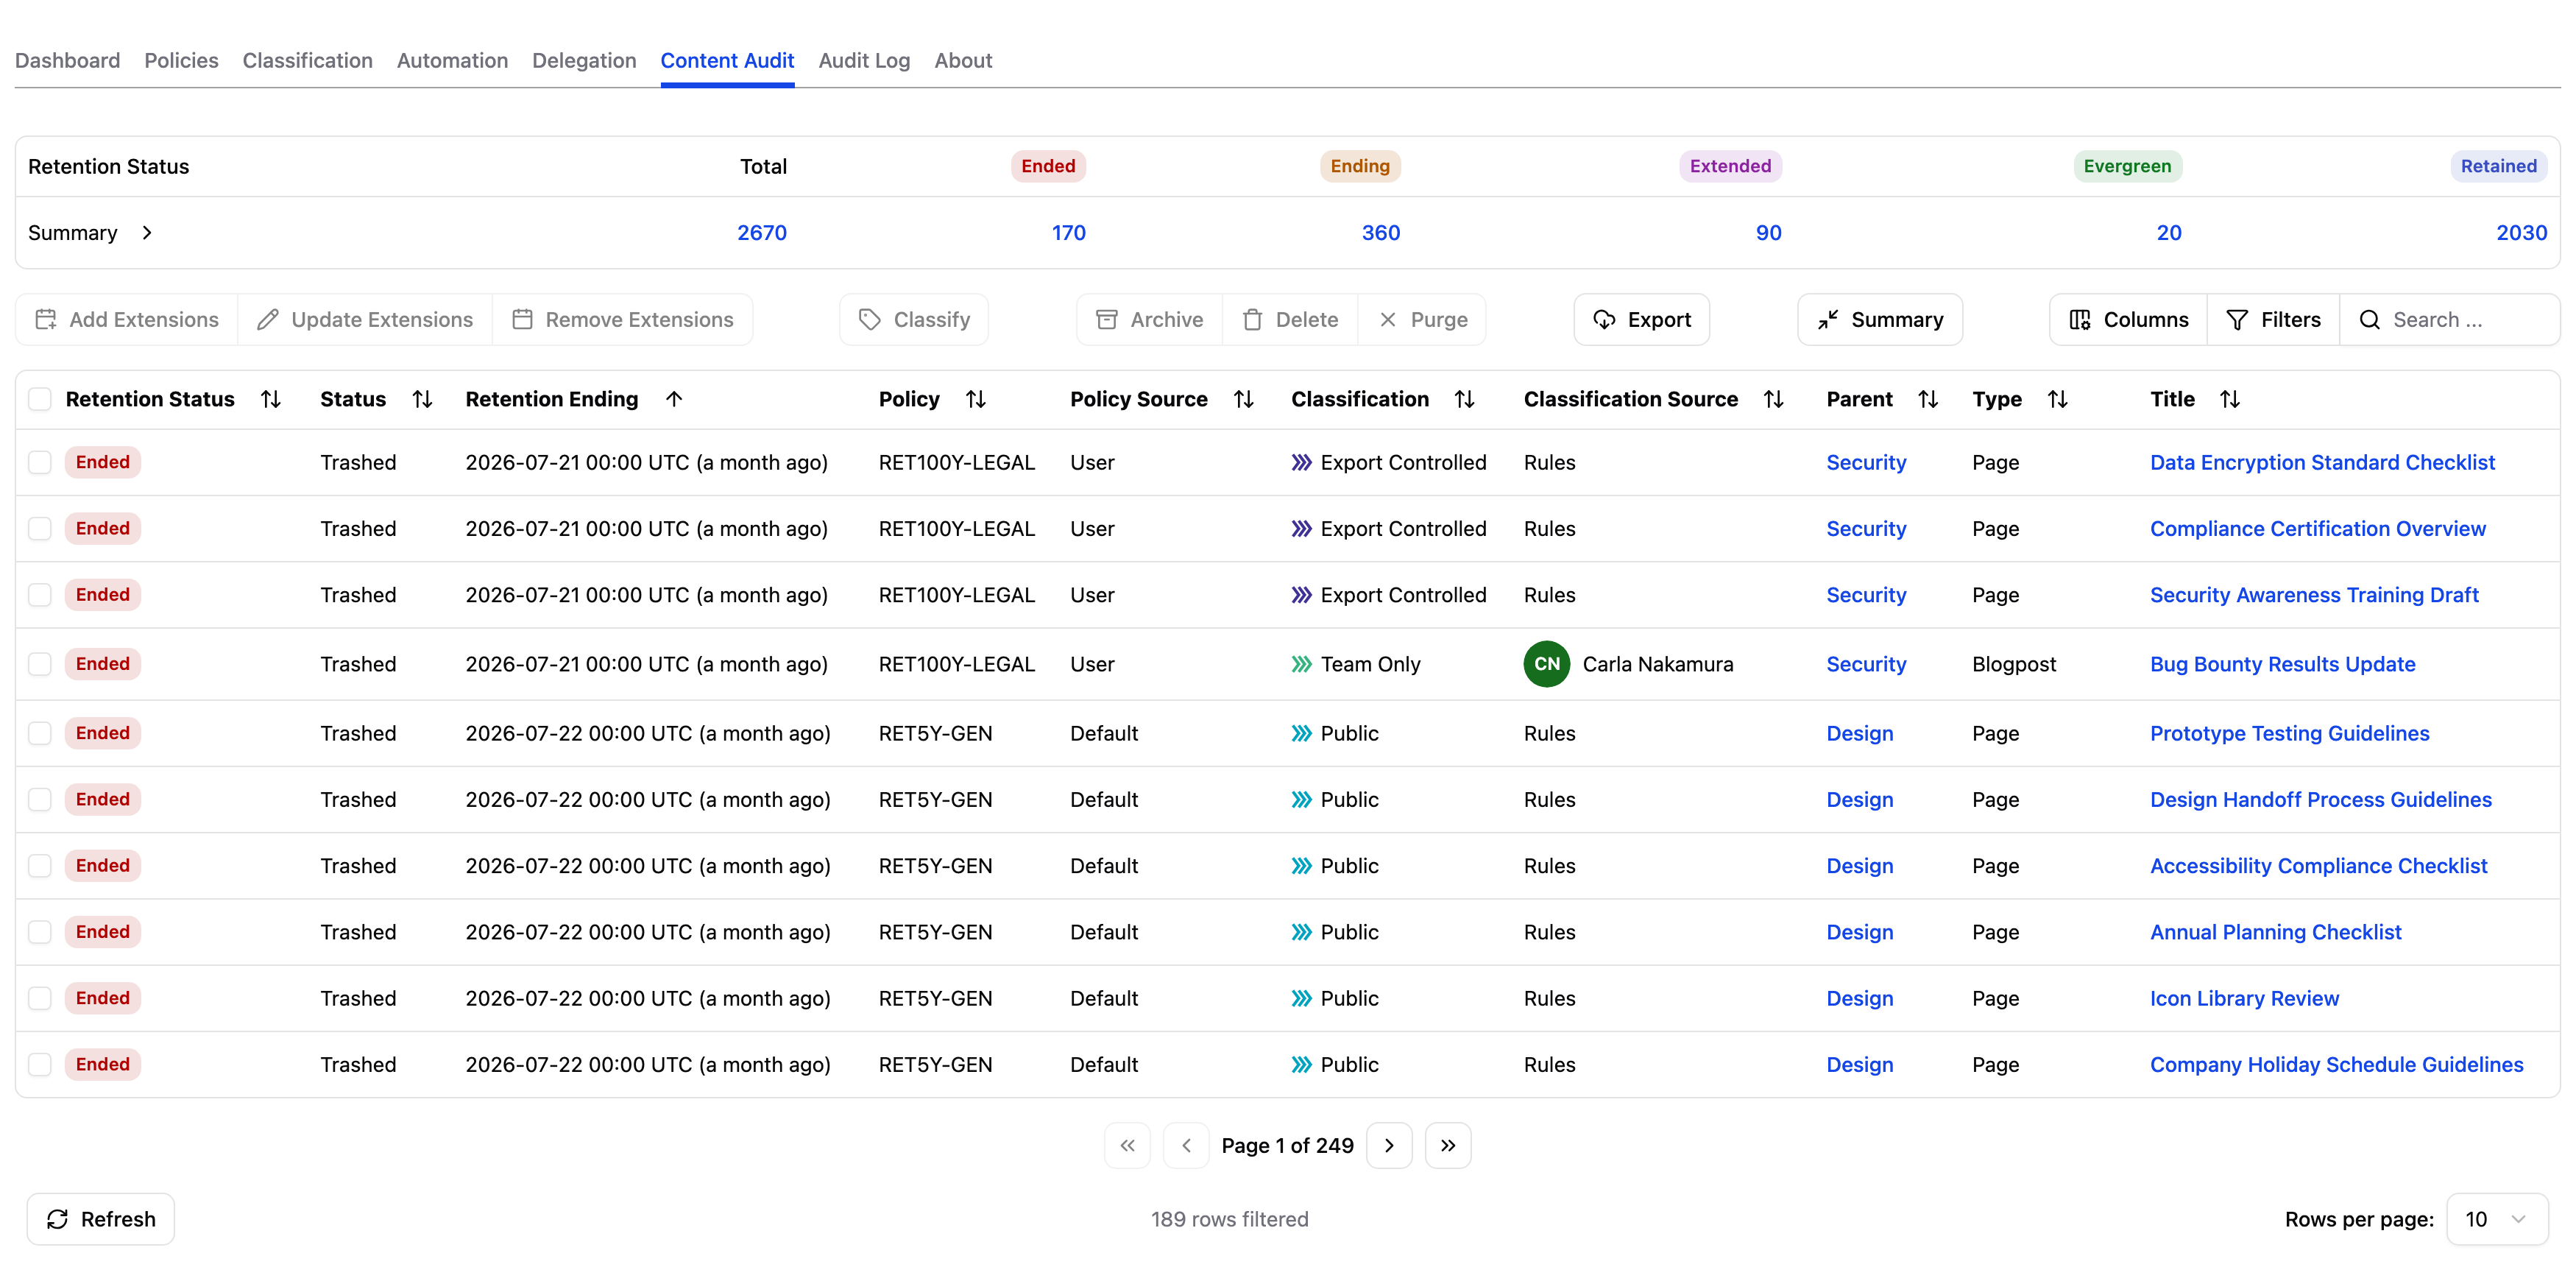
Content Audit table with Policy Source and Classification Source columns enabled
Filtering and Searching
With thousands of items in the audit table, you'll want to quickly find what matters. Use the filter buttons above the table to narrow by specific criteria, or Search for keyword matching across content names.
Four filters are pinned to the toolbar by default: Retention status, Status, Applied policy, and Classification level. Click More filters to add any of the others. Click a filter button to open its options, then check the values you want. Selections apply right away, so there's no separate Apply step:
- Retention status: Filter by Retained, Ending, Ended, Extended, or Evergreen. Start here if you're looking for content approaching or past its retention deadline.
- Status: Filter by Current, Trashed, or Archived. Use this to find content that has been moved but not yet purged. Lite edition doesn't list trashed content.
- Applied policy: Filter by the retention policy code (e.g., RET3Y-COMM) to see how a specific policy is affecting your content.
- Policy Source: Filter by which rule produced the applied policy: Default, Space, Classification, User, or Group.
- Classification level: Filter by sensitivity level (e.g., Internal, Confidential, Restricted) to audit whether sensitive content has the correct retention treatment.
- Classification source: Filter by AI Agent, User, or Rules to distinguish between automatically assigned, user-set, and rule-inherited classifications.
- Flag: Filter by a specific flag, or by Not flagged, to find content that users have marked for attention. See Reviewing Flagged Content.
- Version History: Filter by content that has expired versions or has no expired versions. Available in Standard edition only.
- Parent: Filter by space.
- Type: Filter by Page or Blogpost.
- Owner: Filter by up to 50 specific content owners. Unlike the other filters, leaving this empty shows content regardless of owner.
Every filter also has an equals/not equals toggle in its options popup, so you can narrow to the values you check or exclude them instead. A filter added from More filters can be removed by clicking the x next to it; the four pinned filters stay on the toolbar, but you can reset everything at once with Clear filters, which appears whenever a filter is active.
Applied policy, Classification level, and Parent are each capped at 50 selections, matching Owner's existing limit. When a filter reaches its cap, the dropdown shows a Limit reached indicator and blocks further selections until you remove one.
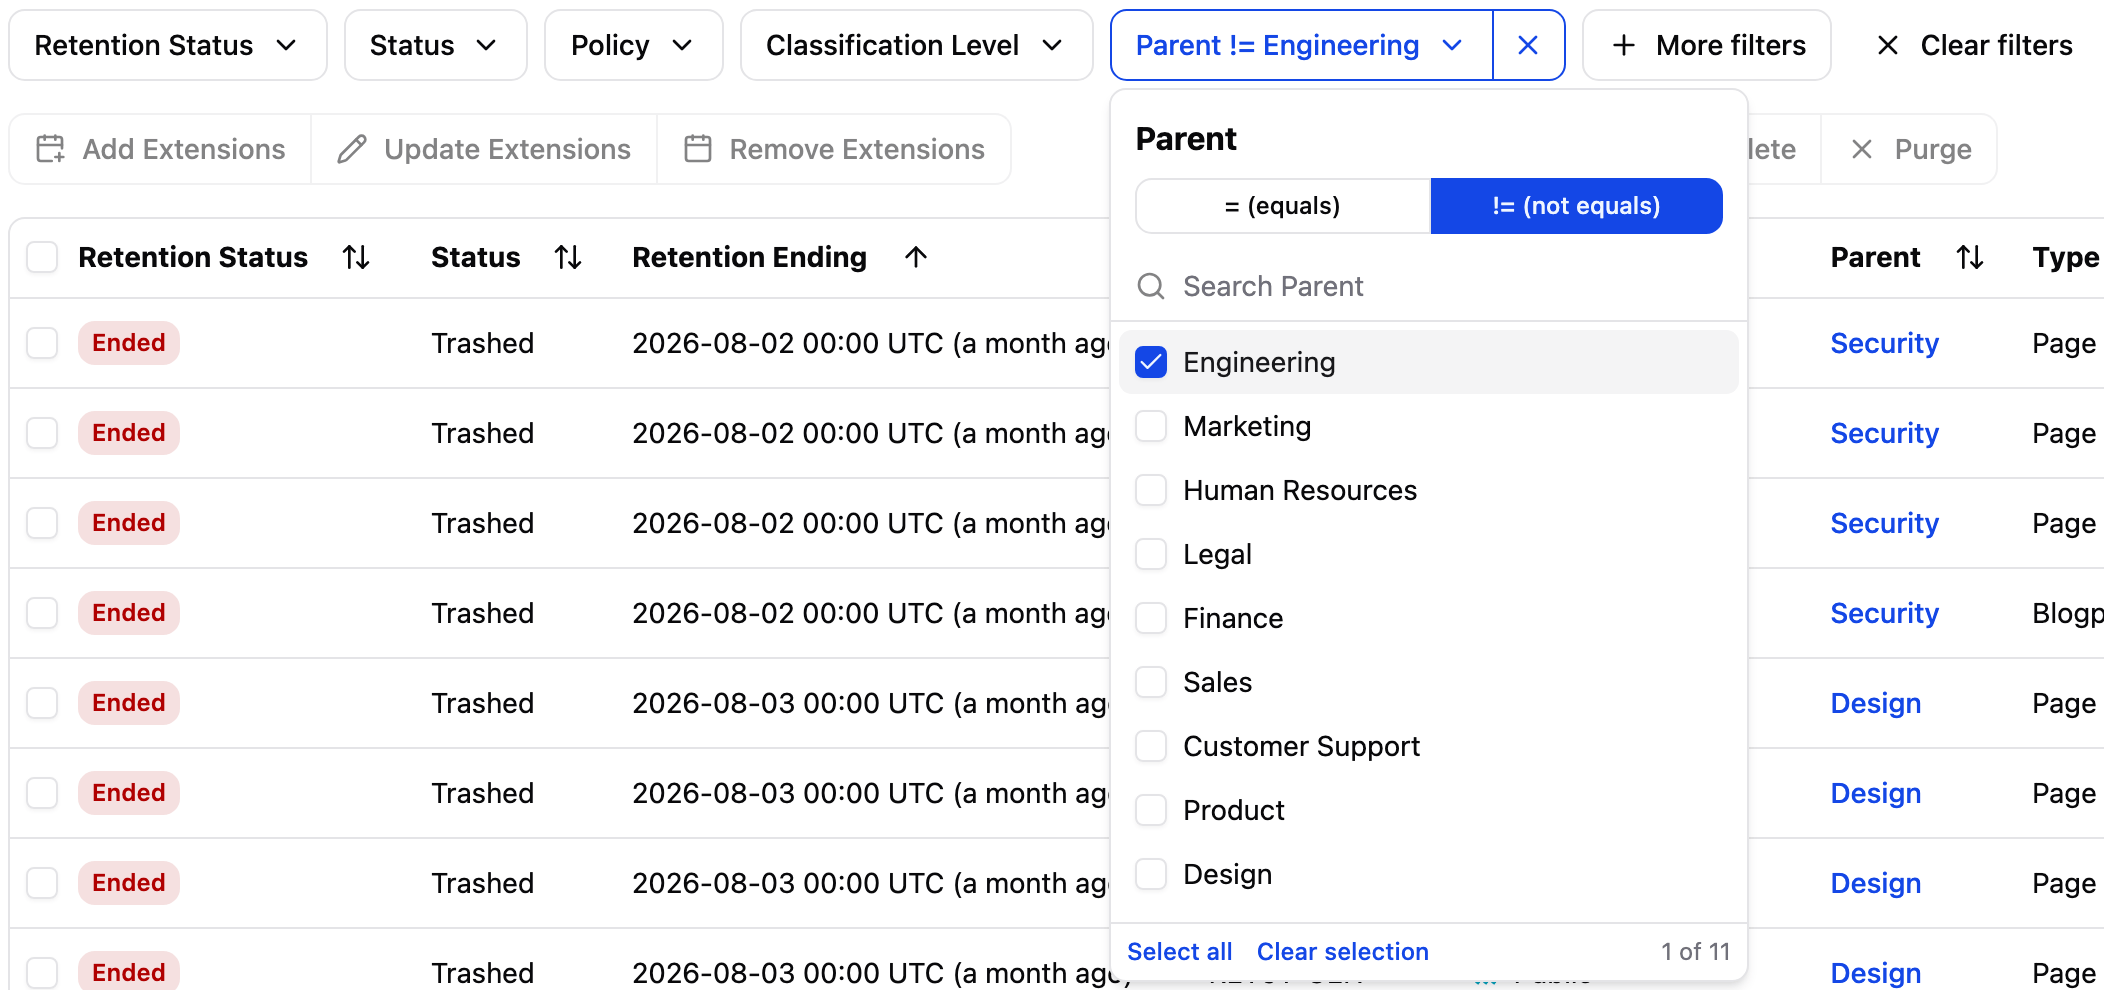
Filtering the Content Audit table by Parent
For keyword searches, use the Search box next to the filter toolbar. It matches your input against the text displayed in each row, including parent space names and content titles, so you can quickly find specific pages or blog posts without knowing their exact name.
Managing Extensions
Select one or more items and use the extension buttons to manage their retention periods:
- Add Extensions: extend the retention period for selected content. Two extension types are available: * Indefinite (evergreen): marks content so it never expires against a retention policy. * Extend to a specific date: sets an explicit future expiration date for the content.
- Update Extensions: modify the date or type of an existing extension on selected items.
- Remove Extensions: remove an extension, returning content to its policy-governed retention period.
Info
Extensions apply to individual items and take precedence over all policy settings, including retention rules.
Lite edition limits the total number of extensions to 100.

Extending a page to a specific date
Classifying Content
This feature is not available in Lite edition of the app.
Select one or more items and click Classify to assign a classification level directly from the audit table. This is the bulk equivalent of the per-content classification feature available to users on individual pages. Like the per-content panel, it overrides any classification rule for each selected item. Use this when your audit reveals items that are misclassified or not yet classified, and you want to correct them without opening each page individually.
To change a single item's level, use the level picker in the Classification Level column instead. It lists the levels you can assign, plus Use inherited, and saves your choice immediately.
Archiving, Deleting, and Purging Manually
This feature is not available in Lite edition of the app.
Danger
Purging is irreversible. Content cannot be recovered after it has been purged.
The Archive, Delete, and Purge buttons let you act on specific items from the audit view, without waiting for automation.
- Archive: moves selected content to an archived state. Requires Confluence Premium or Enterprise. Use this for content in Ending or Ended status that should be preserved but made inactive.
- Delete: moves selected content to the trash. Content remains recoverable by space and Confluence administrators.
- Purge: permanently removes selected content from your Confluence instance.
Each button opens a confirmation dialog listing the selected items before it proceeds.
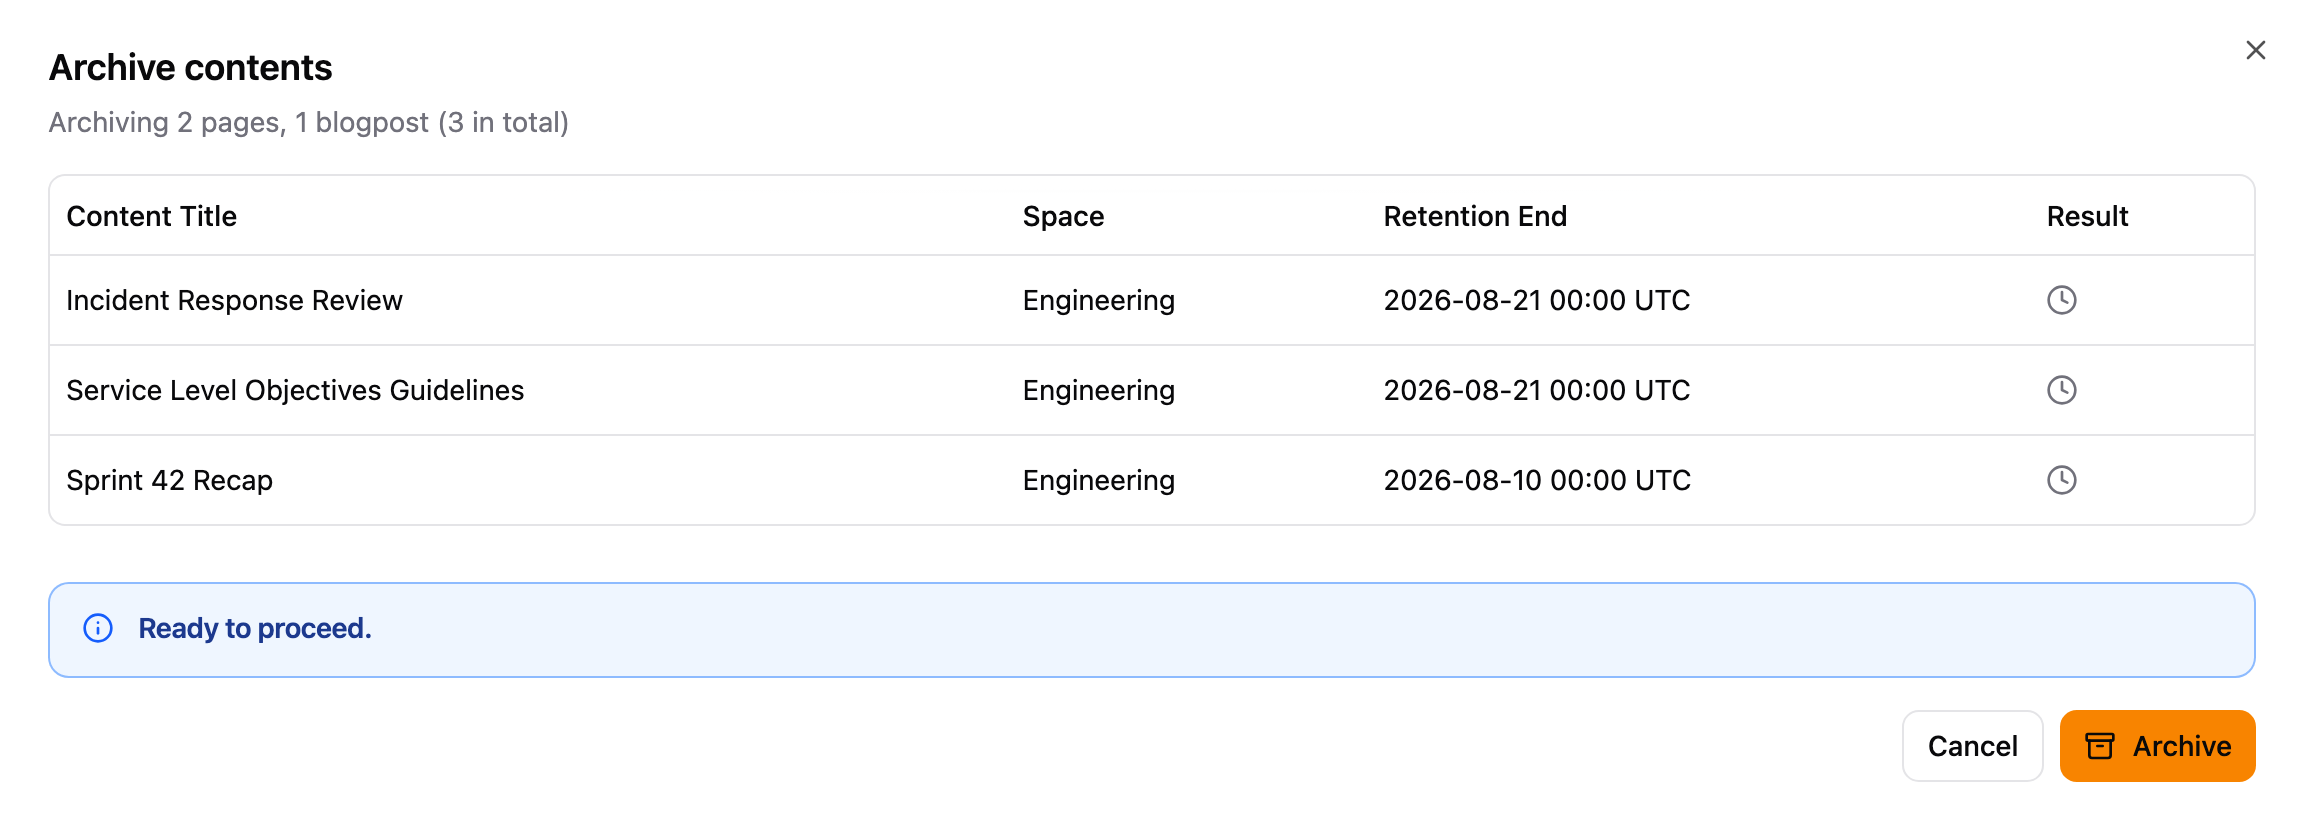
Archive contents confirmation dialog
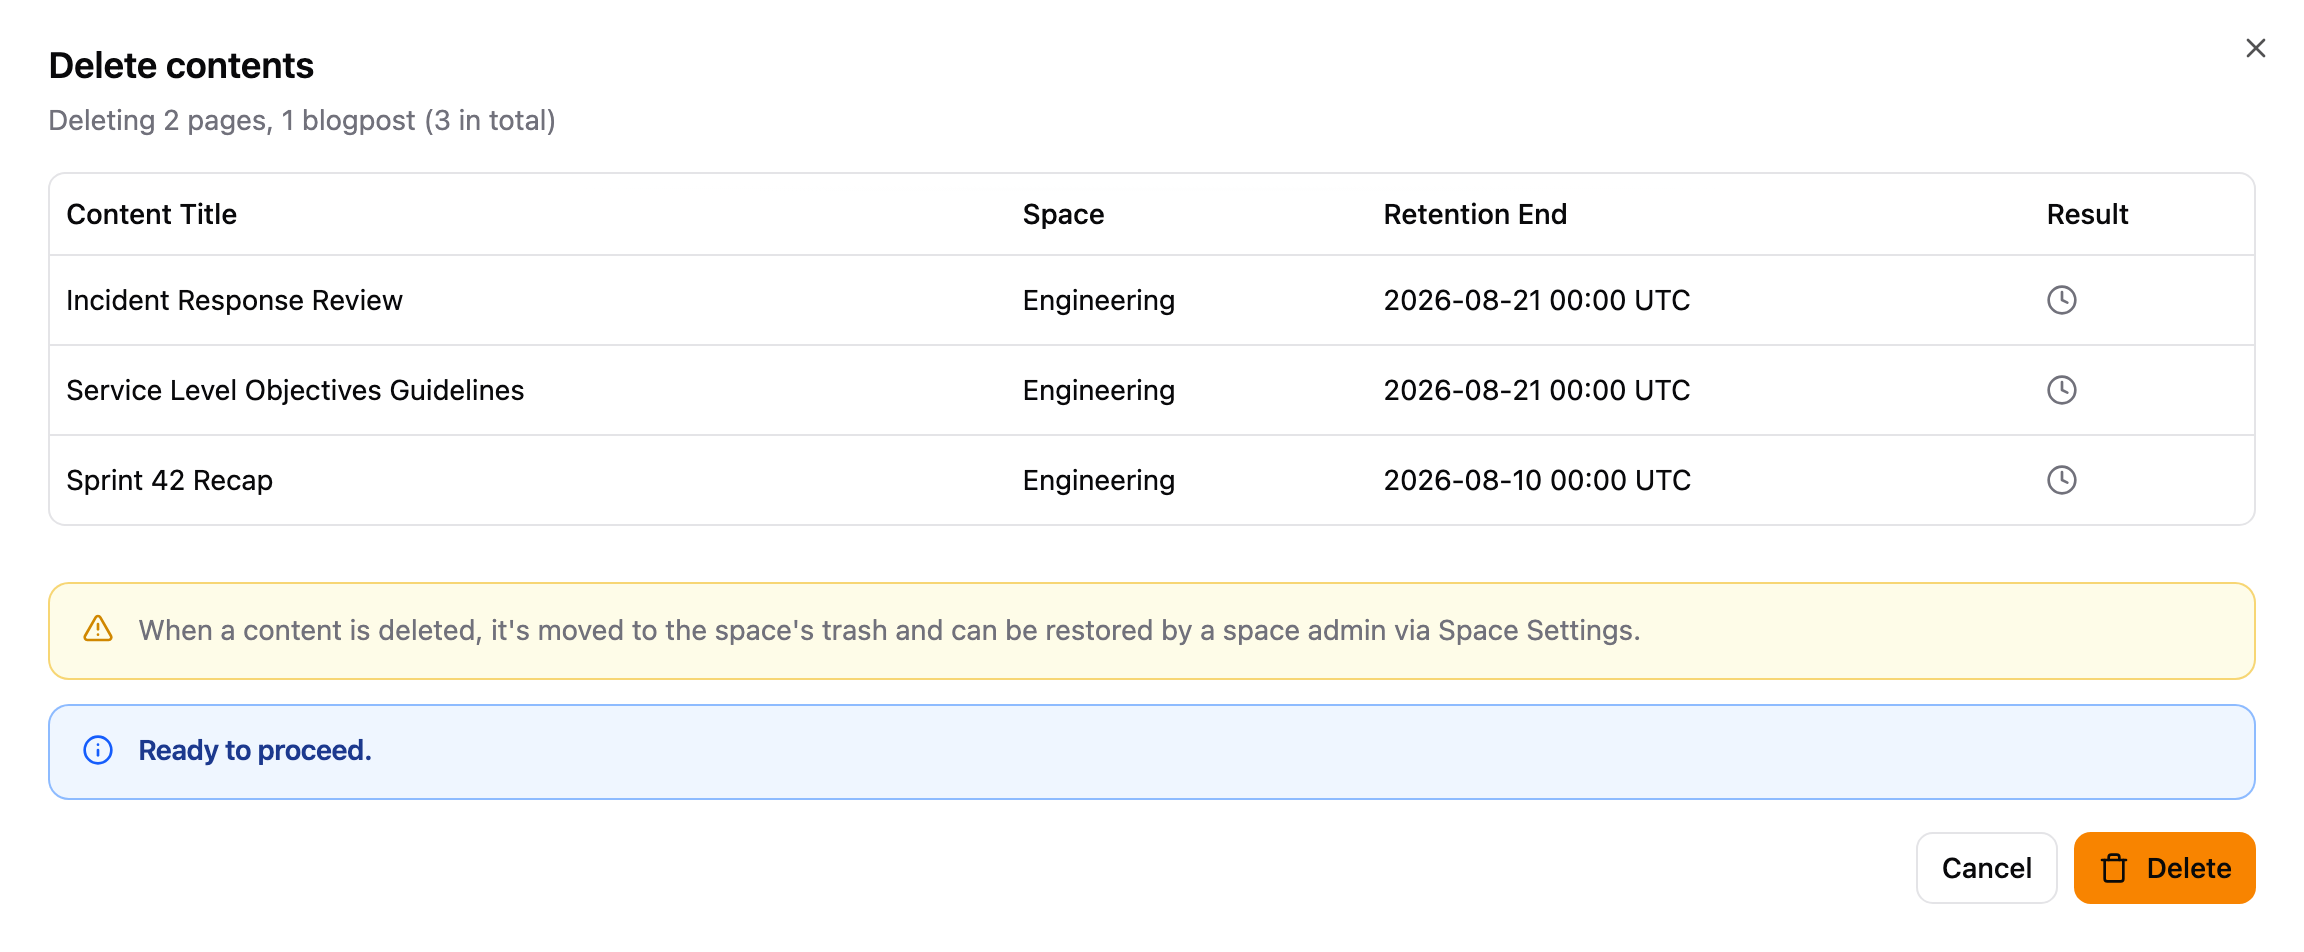
Delete contents confirmation dialog
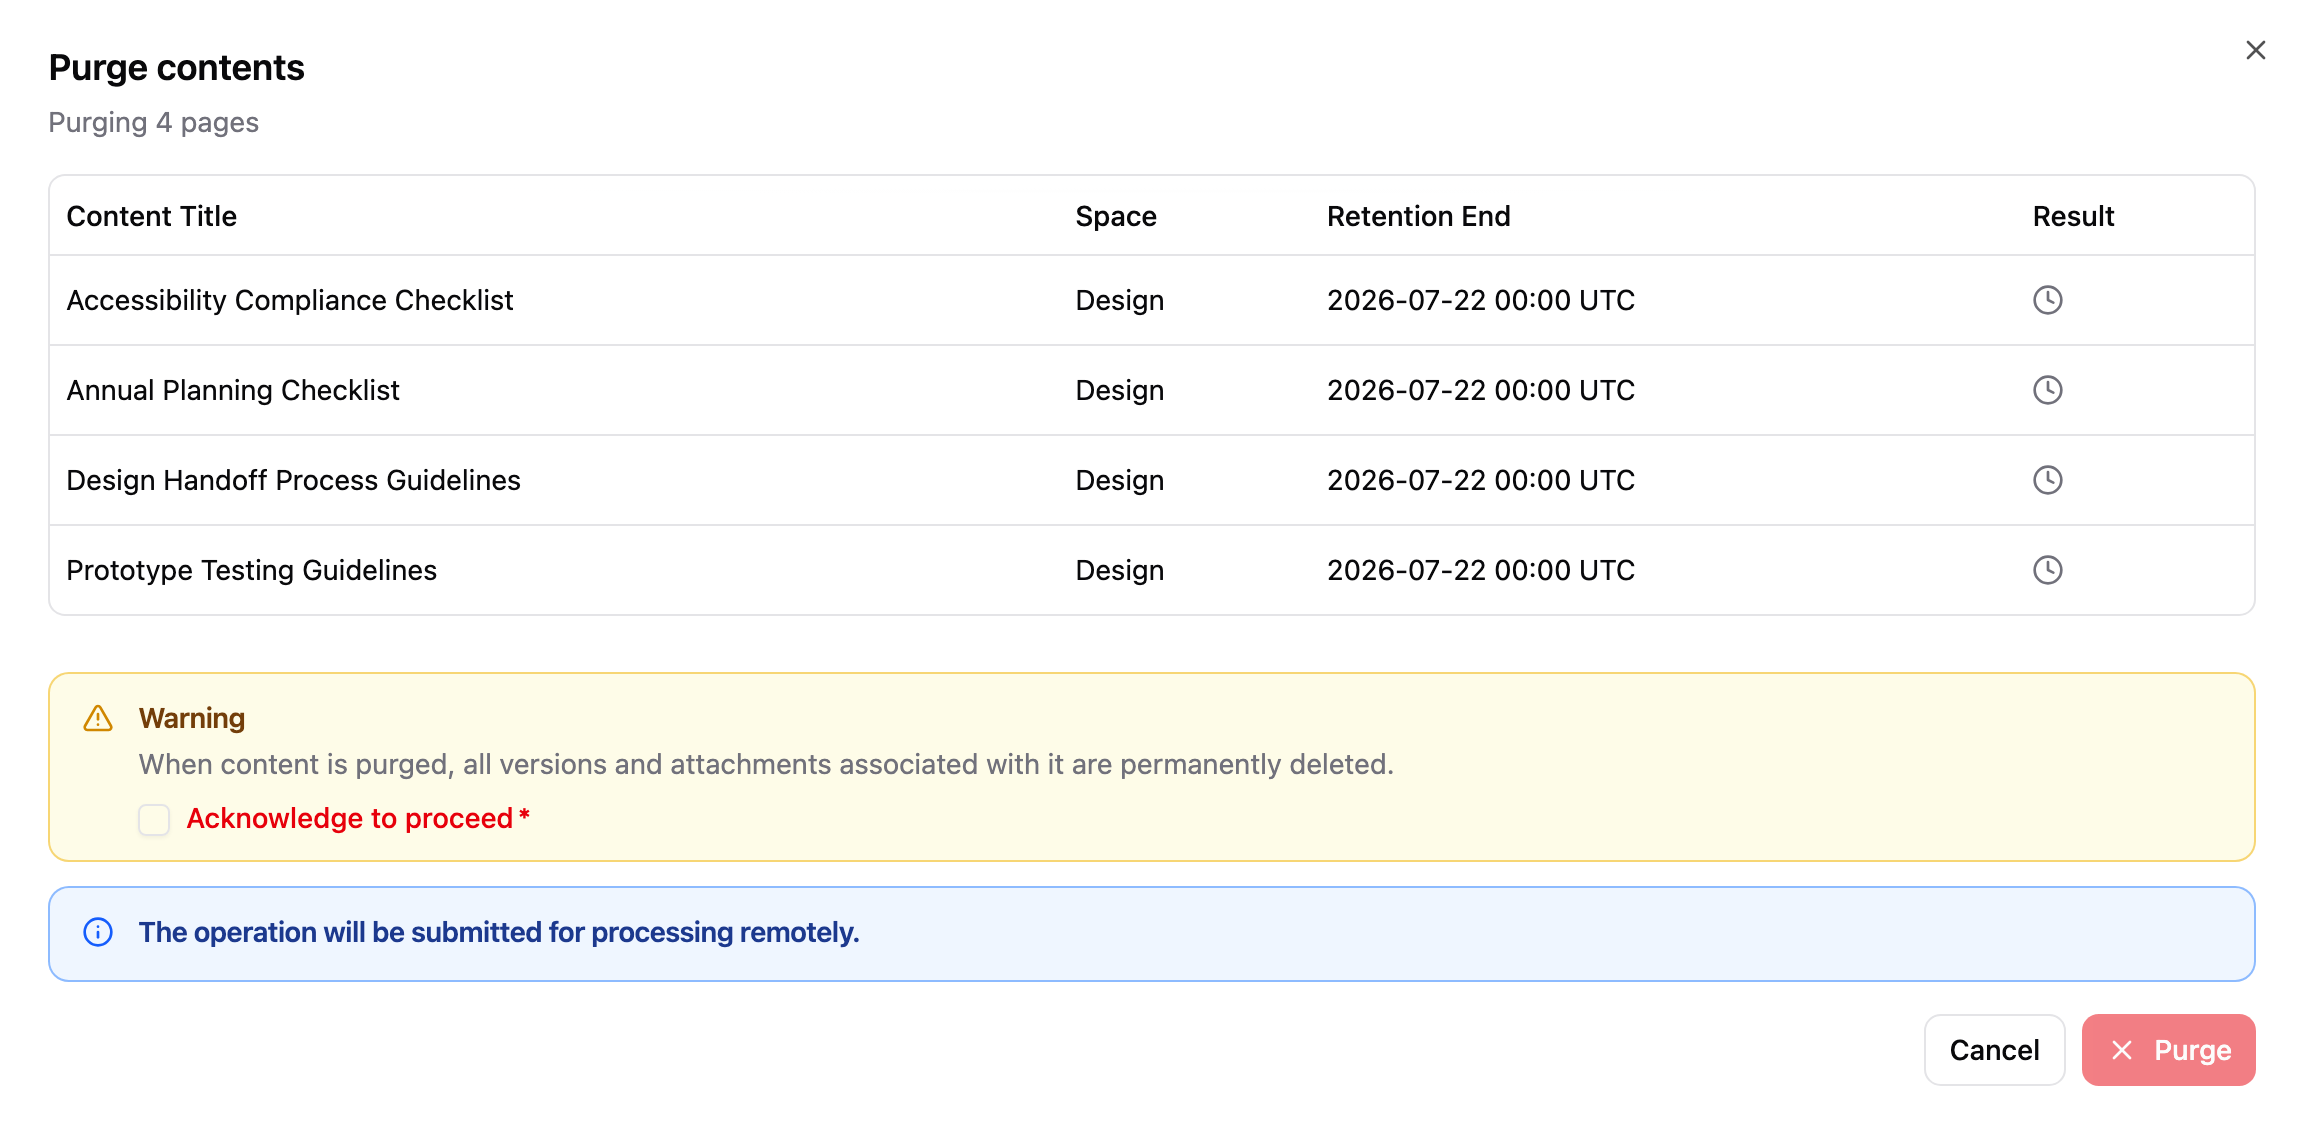
Purge contents confirmation dialog, requiring acknowledgment before proceeding
These are the manual counterparts to the automated archiving, deletion, and purging configured on the Automation tab.
Reviewing Flagged Content
Use the Flag column and filter to work through content that users have marked for attention.
- In the Content Audit tab, click More filters and select Flag.
- Open the Flag filter, click Clear selection, then check the flags you want to review, such as Removal. All options start checked, including Not flagged.
- Hover over the icon in the Flag column to see the flag's name, its reason, who flagged the content, and when.
- Select the items you want to act on, then use the buttons described in Managing Extensions and Archiving, Deleting, and Purging Manually. For example, extend content that is still needed, or archive content that should go.
- To remove a flag without acting on the content, open the content from the Title column and clear the flag from its panel, as described in Clearing a Flag.
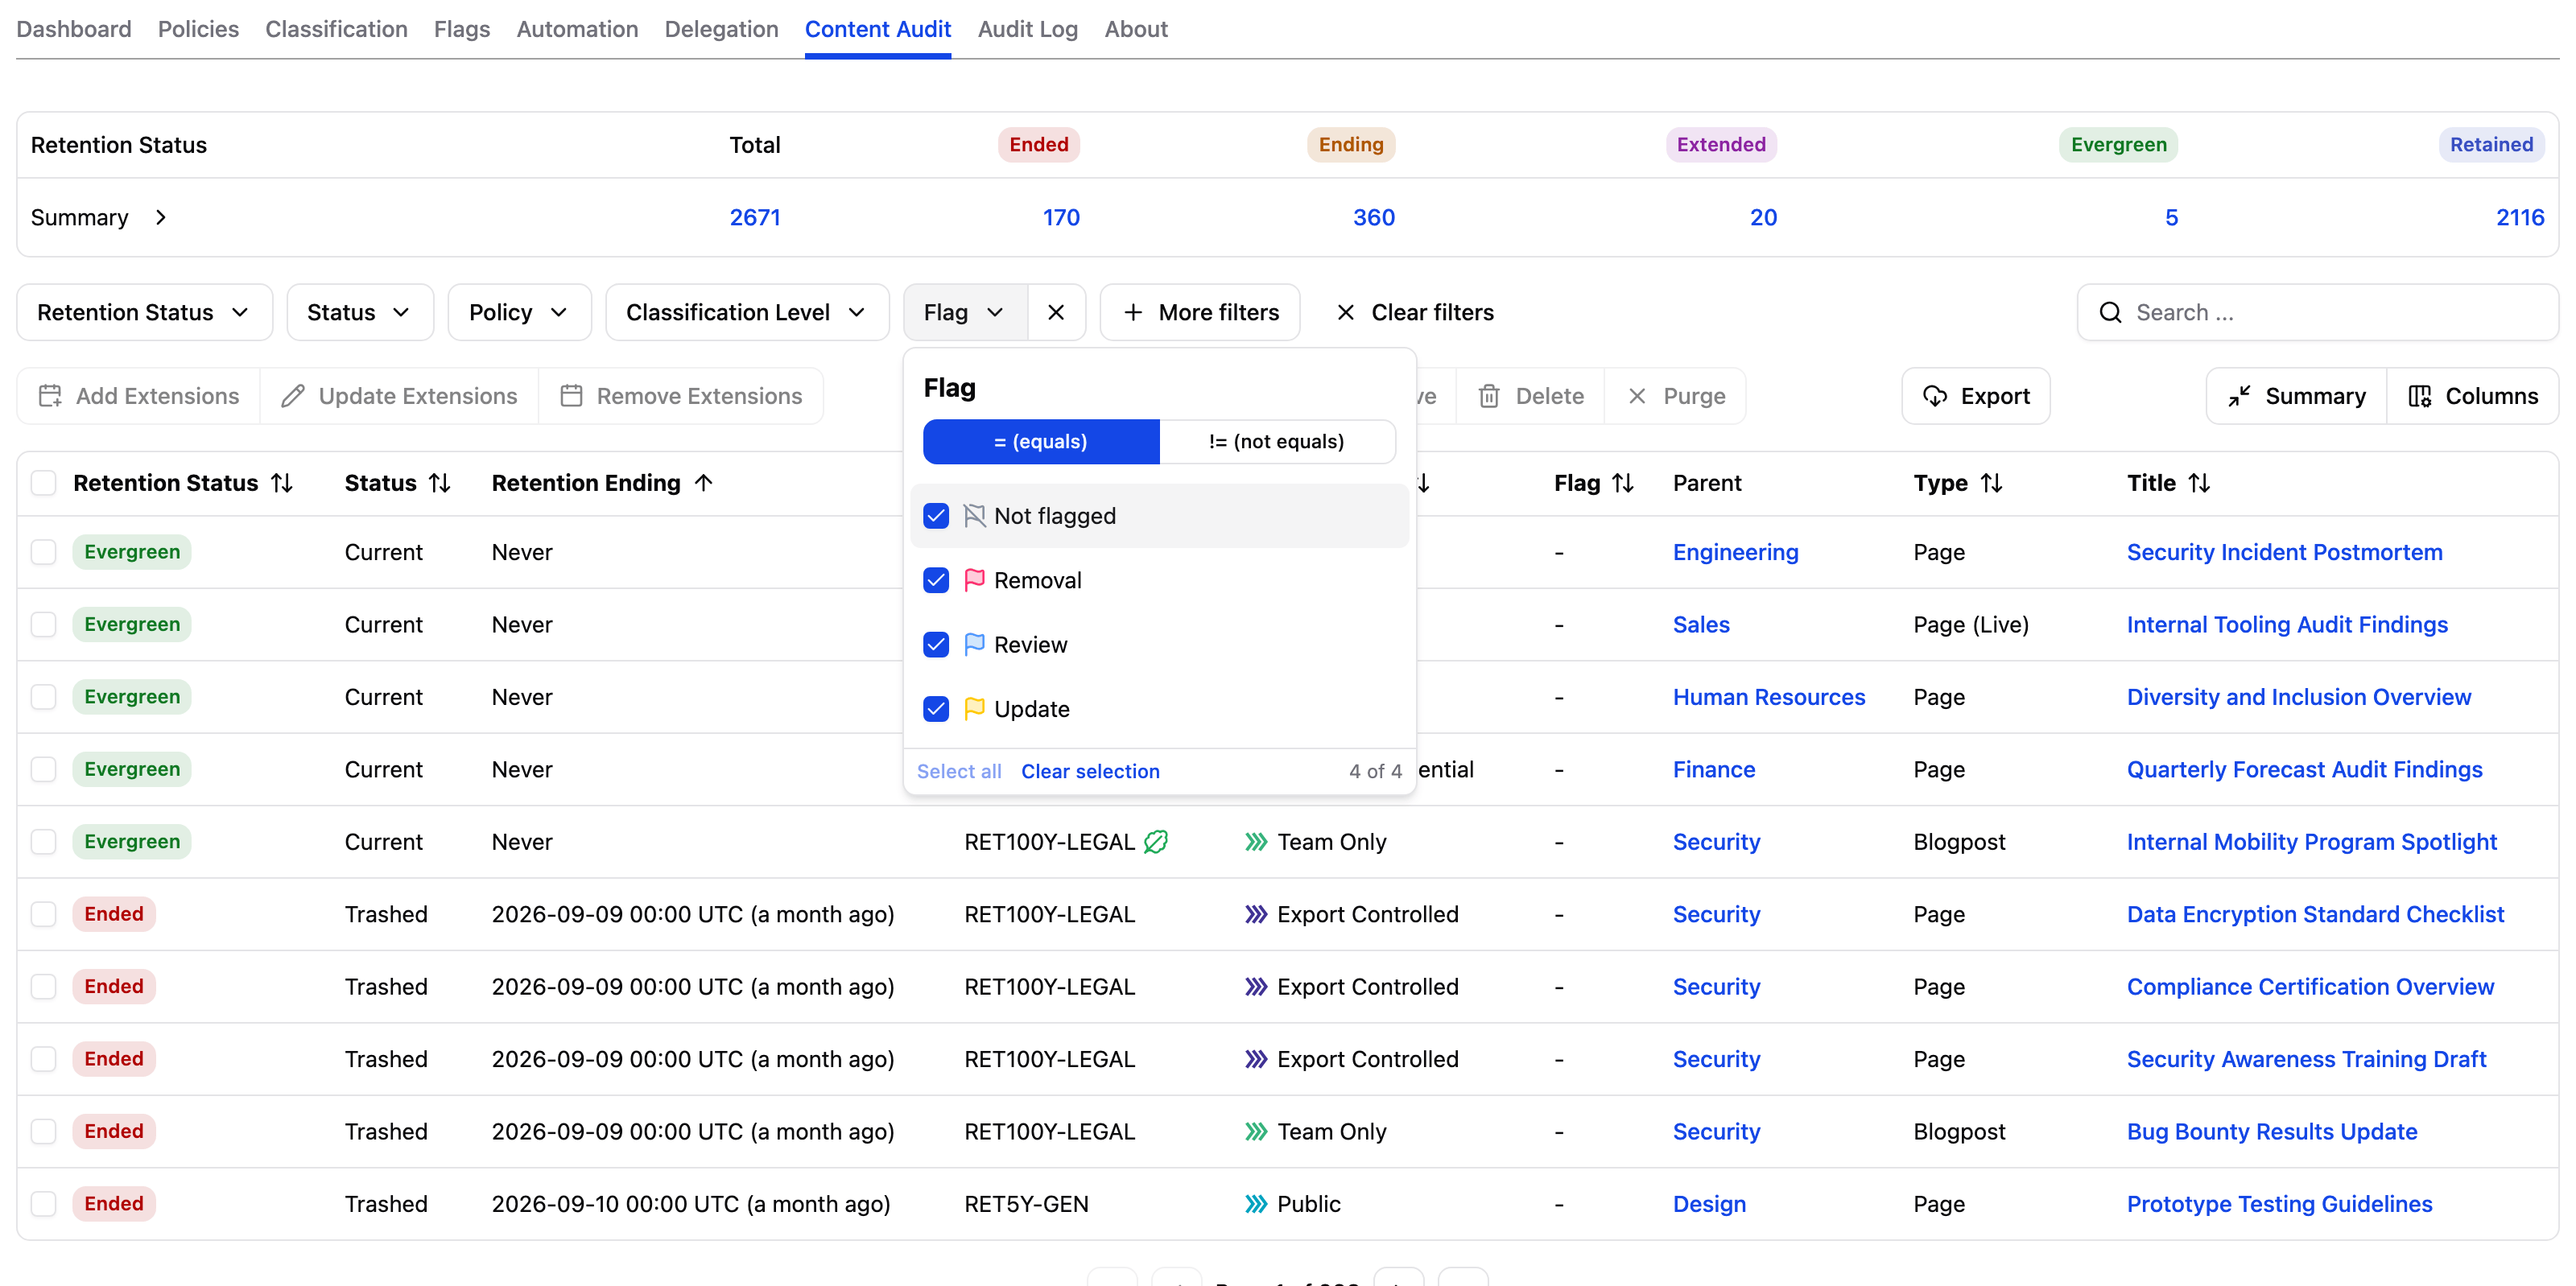
Filtering the Content Audit table by Flag
Non-admin users see the Flag column and filter only when Allow users to view flags and un-flag content is on.
Automation
This feature is not available in Lite edition of the app.
Use the Automation tab to configure three features: retention enforcement (archiving, deletion, purging, and version pruning), audit log retention, and automated classification with AI. Each feature operates independently and can be enabled or disabled without affecting the others.
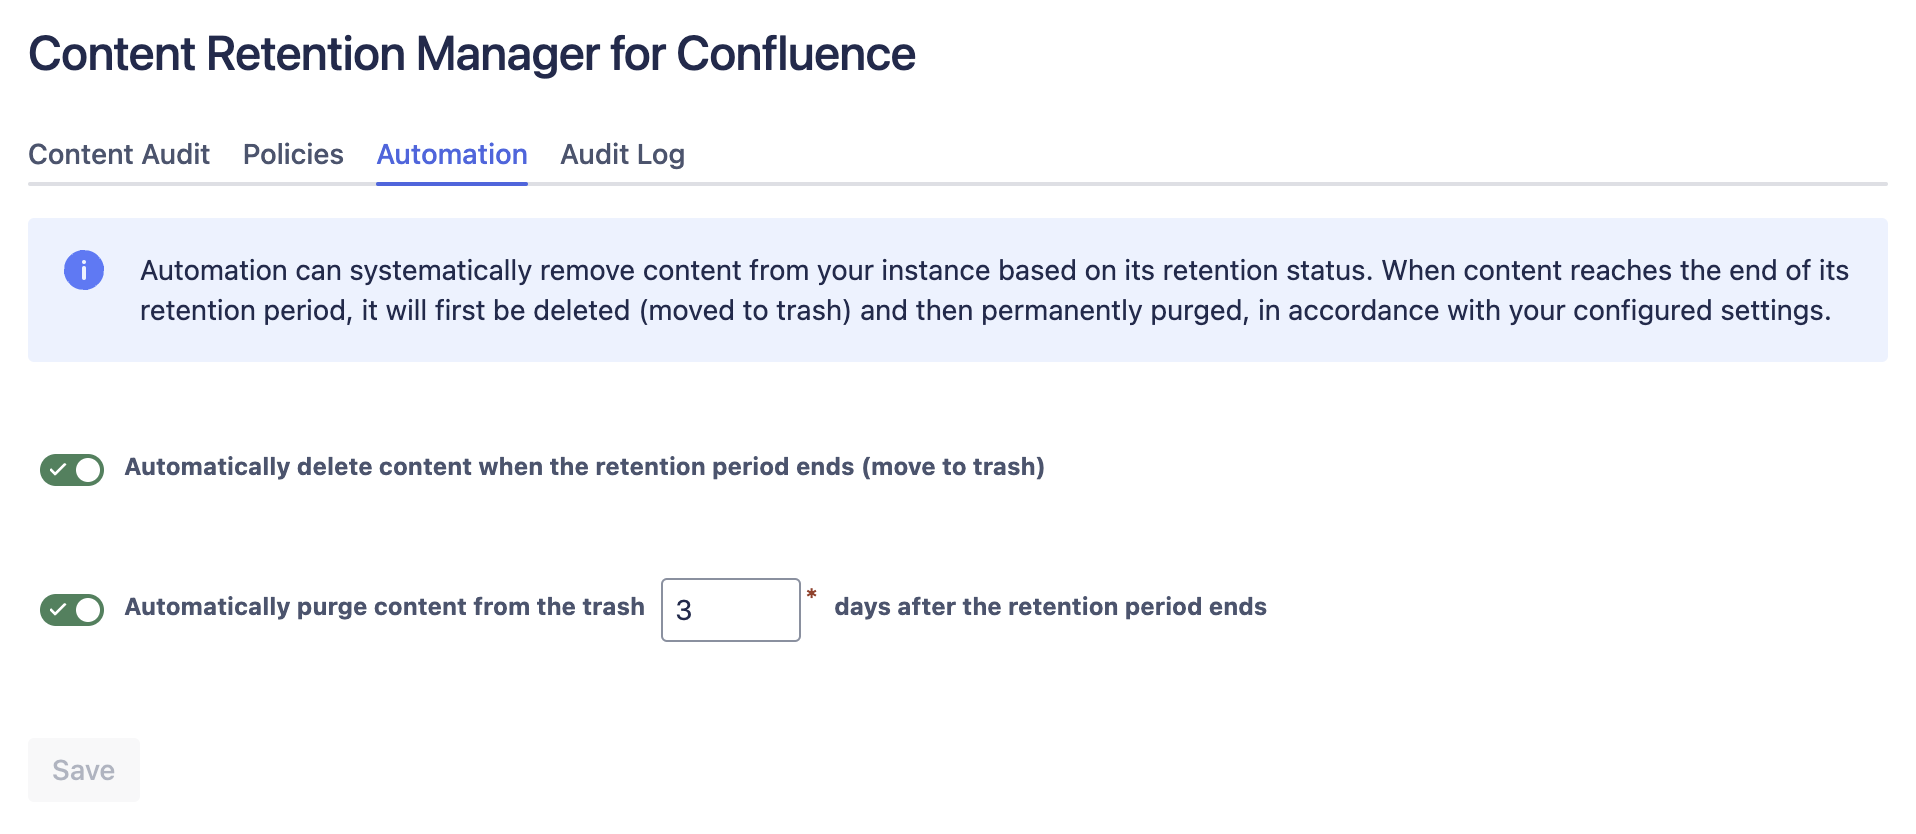
The Automation tab in Content Retention Manager for Confluence
Retention Enforcement
Danger
Once automation is on, expired content will be archived, deleted, or purged according to your policies. Purged content and pruned page versions cannot be recovered.
Before enabling automation, complete a thorough review using the Content Audit tab. Verify that your retention policies and classification rules are producing the results you expect, update any rules that need adjustment, and apply extensions or per-content classification overrides for anything that needs special handling.
The Retention Enforcement section lets you schedule the retention lifecycle:
- Automatic archiving: When content enters the Ending status (during the configured warning period before retention ends), it can be automatically archived.
- Automatic deletion: When content expires against the retention policy, it can be automatically deleted. Deleted content is not visible to regular users but remains recoverable by space and Confluence administrators.
- Automatic purging: When content reaches the end of its retention period, it is purged after a configurable delay. Purged content is irrecoverable and no longer discoverable.
- Automatic version pruning: When a historic version of a page or blog post reaches the end of its retention period, it can be permanently deleted (pruned). The current version is never pruned, archived content can't be pruned, and the Audit Log records each pruned page.
- Click the Automation tab.
- Under Retention Enforcement, enable Automatic archiving if you want content archived when it enters the Ending status.
- Enable Automatic deletion if you want content deleted when it expires.
- Enable Automatic purging if you want content permanently removed after the delay period.
- Set the Purge delay after the retention period ends (days). A few days provide a buffer in case content that should have been retained was not flagged in time.
- Enable Automatic version pruning if you want historic page and blog post versions deleted when they reach the end of their retention period.
- Set the Prune delay after a version is replaced (days). The app prunes a version only after this many days have passed since a newer version replaced it, so a recent edit doesn't remove the previous version of a long-dormant page.
- Click Save.
To see which pages have versions past their retention window, use the Version History filter and column in the Content Audit.
Audit Log Retention
In the Automation tab overview above, locate the Audit Log Retention section to control automatic cleanup of old audit log entries:
- Toggle Audit log retention to ON.
- Set Retain audit logs for (days). The minimum is 30 days.
- Click Save.
When enabled, entries older than the configured period are automatically deleted. Disable this setting to keep all audit log entries indefinitely.
Automated Classification with AI
This feature is not available in Lite edition of the app.
Content Retention Manager uses AI-powered classification to automatically assign sensitivity levels to content. In the Automation tab overview above, locate the Automated Classification section to enable the feature and set up the automation flow. The system uses Confluence Automation to invoke the AI Classification Agent whenever pages are published or updated.
The agent analyzes page content and recommends a classification level on your behalf. When users open a page with an AI-assigned classification, they see the classification level in the byline item suffixed with (AI) (for example, Restricted (AI)). Users with permission to set classifications can click the byline item to review the AI assignment and either confirm it or reject it and select a different level.
When a user confirms the AI assignment, the (AI) suffix is removed and the classification is recorded in the audit log as updated by the user. See AI Classification Suggestion in the User's Guide for the complete end-user experience.
Classifications take effect immediately
Classifications assigned by the agent are applied immediately and may affect the content's retention lifecycle.
Tip
Confluence Automation has a monthly rule run quota on non-Enterprise plans. Using Page edited gives continuous re-classification as content changes, but consumes more runs than a Page published trigger. See Confluence Automation limits for current limits.
Set up automated classification with AI in two steps: enable the feature in Content Retention Manager, then create a Confluence Automation flow to invoke the agent.
Enable Automated Classification
- Click the Automation tab.
- Under Automated Classification, toggle Auto Content Classification Agent in Automation to ENABLED.
- Click Save.
Set Up a Confluence Automation Flow
With the feature enabled, create a global Confluence Automation flow that invokes the agent. This setup follows Atlassian's Automating Rovo agents guidance for the Use agent action.
-
In Confluence, open Settings → Automation.
-
Click Create flow, then Create from scratch.

Create a new Automation flow from scratch in Confluence
-
Add the trigger Page edited.

Add the Page edited trigger to run classification when a page is updated
-
Click Add action, then select Use agent in the Rovo AI section.

Select the Use agent action from the Automation action picker
-
If prompted, connect Automation to Rovo by clicking Connect.

Connect Atlassian Automation to Rovo before selecting an agent
-
In Use agent, search for and select Auto Content Classification (Confluence).

Search and select the Auto Content Classification (Confluence) agent
-
In the Prompt field, enter:
contentType={{content.type}}, contentId={{content.id}}Critical for page identification: The
{{content.type}}and{{content.id}}Confluence smart values tell the agent which page triggered the automation and needs classification. Without these identifiers, the agent cannot locate the target page.
Configure the Use agent prompt with content type and content ID smart values
-
Add a Log action step after Use agent to record the agent output in the Automation run details.
-
In Log action, set Log message to:
(Type={{content.type}}, ID={{content.id}}) {{agentResponse}}The
{{agentResponse}}reference contains the Auto Content Classification agent's response, which describes the recommended classification level for the page (for example, Restricted or Internal). This response is recorded in the Confluence Automation audit log. The agent also creates a corresponding entry in the Content Retention Manager Audit Log showing the classification applied, providing a complete audit trail of the automation decision.
Configure Log action to record content identifiers and
{{agentResponse}} -
Click Save and enable, set the flow name, then click Turn on flow.

Save and enable the flow after configuring trigger and actions
Validate and Troubleshoot
To verify that automated classification is working correctly and maintain traceability, review both logs: the Confluence Automation audit log for run execution, and the Content Retention Manager Audit Log for classification outcomes.
In Confluence Settings → Automation → Audit log, confirm runs complete successfully and review step details for Page edited, Use agent, and Log action. This log shows each run trigger, execution status, and agent output.

Automation audit log showing successful execution and step level details
In Content Retention Manager, open the Audit Log tab and filter by the page ID to verify classification updates are recorded. This log shows AI-triggered classification updates from AI Agent, including assigned level and timestamp. It also shows manual user confirmations from the byline. Together, these logs provide end-to-end traceability from run execution to classification outcome.

Content Retention Manager audit log showing AI Agent updates and user confirmation updates
Delegation
This feature is not available in Lite edition of the app.
Delegation allows you to share Content Retention Manager admin access with users who don't hold the Confluence Admin role. Members of delegated groups can manage retention policies, classification levels, automation, and other app settings, including policies that govern content they cannot delete in Confluence, and can read the full Audit Log. Delegate only to trusted users who understand your organization's retention policies.
There are a few key differences between a Confluence admin and a delegated admin:
- Only a Confluence admin can modify delegation settings. A delegated admin can view but cannot change these settings.
- Adding a user as a delegated admin does not alter their Confluence permissions. In the Content Audit tab, a delegated admin can only see content they have read access to in Confluence, and can only use the Purge button on content they could delete in Confluence. However, by modifying policies, classification rules, and definitions, or by enabling automation, a delegated admin can affect the retention and classification of all content on the site, including content they cannot directly access.
- A delegated admin reads the same unfiltered Audit Log as a Confluence admin, including entries for items they have no access to. These entries record item IDs and operations, never content titles or content.
Info
Revoking delegated access, by removing a group from the delegation or removing a user from a delegated group, can take up to 1 minute to take effect.
To review and modify the delegation, click the Delegation tab.

Delegation tab in Content Retention Manager for Confluence
To add groups:
- Click the Add Groups button above the table.
- In the dialog, select the groups to delegate to. Only groups with the User access type (non-admin groups) are shown.
- Acknowledge the warning and click Add Group to confirm.
- Click Save to apply your changes.

Add groups as admin delegates in Content Retention Manager
Notifications
This feature is not available in Lite edition of the app.
Content Retention Manager can notify users while they use Confluence when content they own is ending soon or has already ended. The notification tells them how many items are affected and lets them open their own expiring content in Content Audit. See Content Expiry Notifications in the User's Guide for what users see.
To review and change the settings, click the Notifications tab. The Content expiry section has two settings:
- Content expiry notification: Turn the switch on or off. When it is off, nobody receives the notification and Add Exclusion is unavailable.
- Exclusions: The users and groups who never receive the notification. Members of an excluded group are excluded too, and a change to a group's membership can take some time to apply.
To exclude someone:
- Click Add Exclusion above the table.
- In the dialog, set Type to User or Group, then select who to exclude.
- Click Add to confirm.
- Click Save to apply your changes.
To stop excluding a user or group, click the trash icon at the end of their row, then click Save.
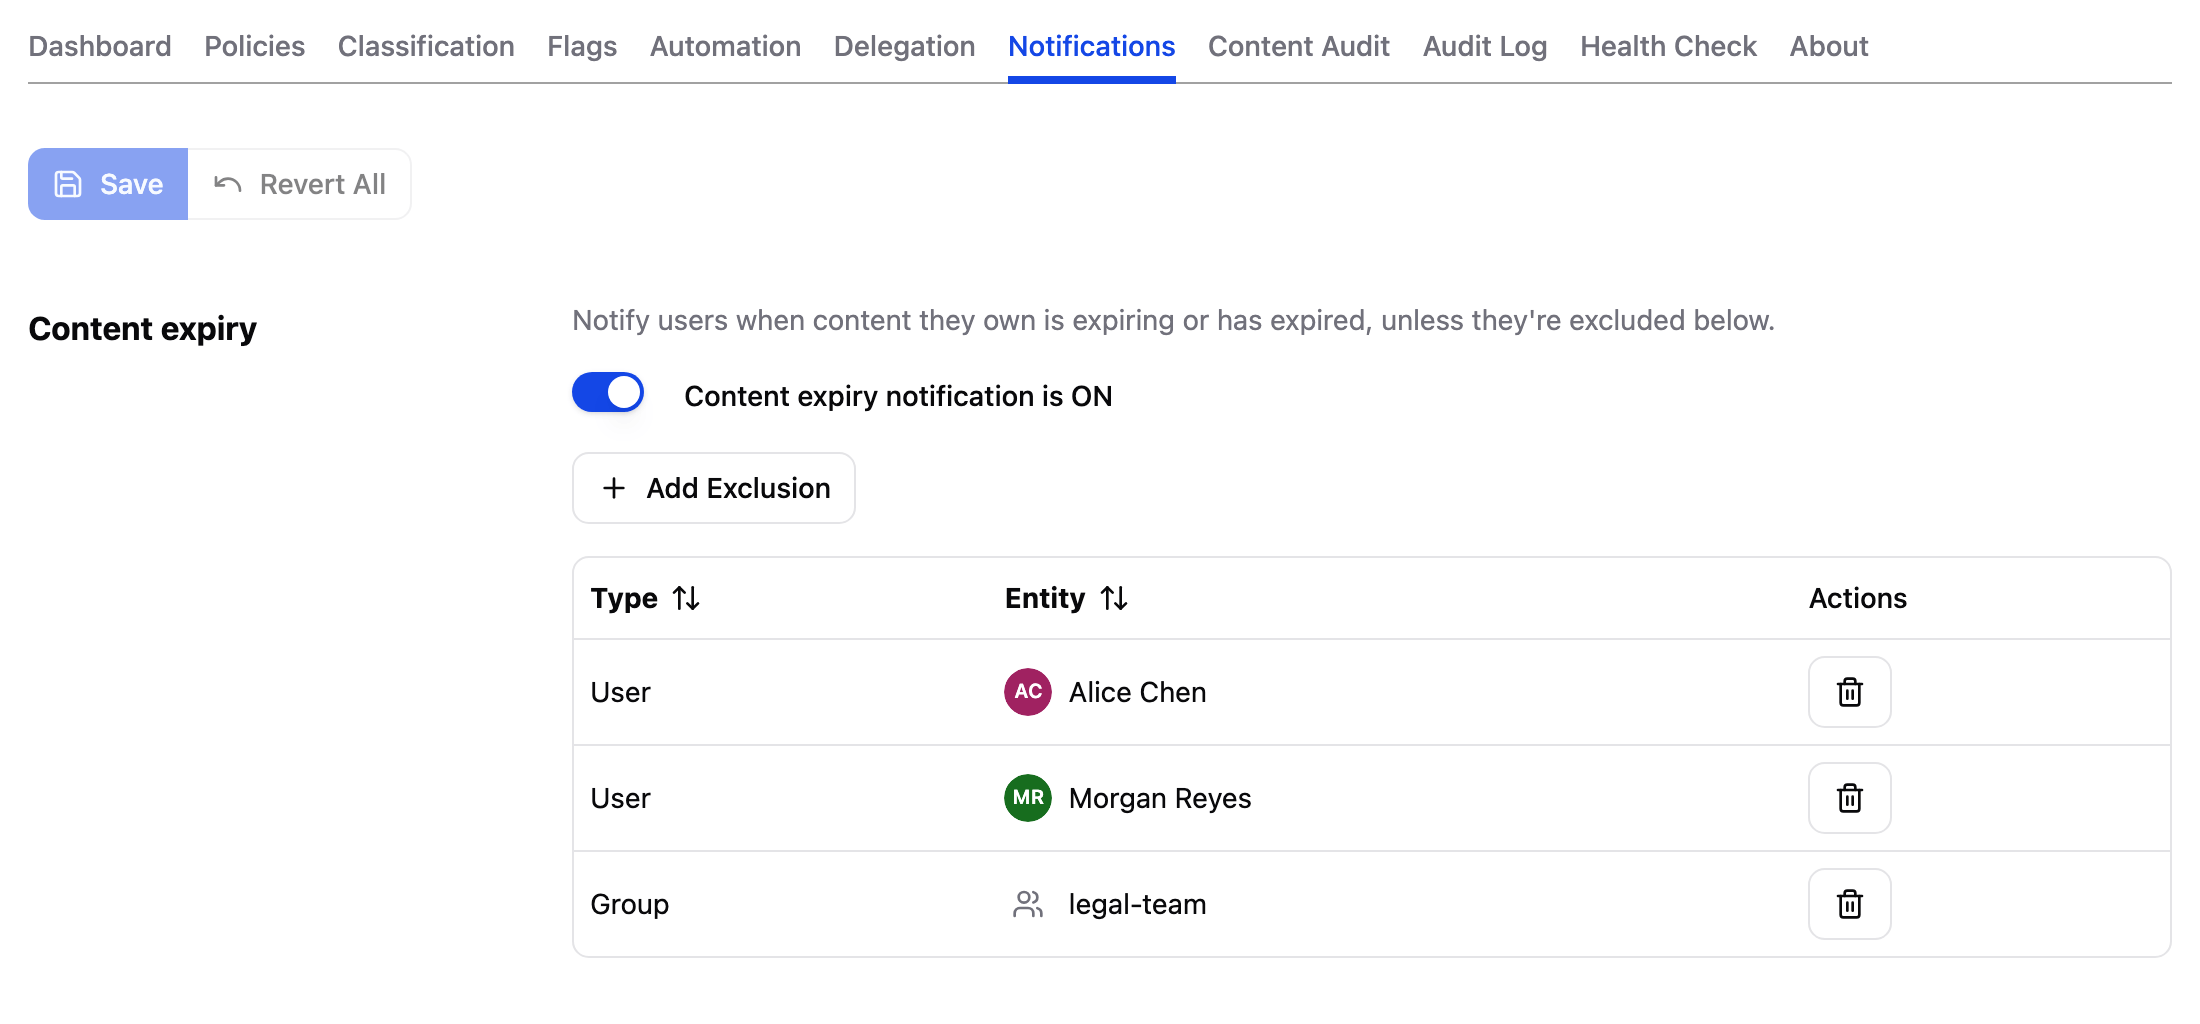
Notifications tab in Content Retention Manager for Confluence
Audit Log
The audit log is a permanent record showing who set or updated a policy, defined an extension, or archived, deleted, or purged content, and when. It also records flag changes, including a flag cleared automatically after an edit. If a page or blog post is archived, deleted, or purged by automation, it appears in the log. The log records content by ID only, not the content itself.
Only Confluence admins and, in Standard edition, delegated admins can read the Audit Log. They all see the same unfiltered log, including Audit Log entries for items they have no access to in Confluence. Each Audit Log entry records the item or setting it applies to, the operation, the account ID of whoever performed it, and a short description of the change. Audit Log entries never include content titles or content.
Entries with an arrow at the end of the row have expandable details. Click the arrow to show or hide them.

Example Audit Log in Content Retention Manager for Confluence
Troubleshooting Permissions
The app runs under its own app user account, and Confluence applies permissions to that account like any other. Three kinds of access control can leave the app user without the access it needs:
- Your organization's data policy, which can block the app from some content.
- Space permissions, which can limit what the app user can do in a space.
- Page restrictions, which can keep the app user from reading individual pages and blog posts.
Typical signs of a gap are pages missing from the Dashboard and Content Audit, and failed automation or bulk actions in the Audit Log. In Standard edition, the Health Check tab checks for all three kinds of access control.
Your organization's data policy can block apps from accessing some content. In Standard edition, the Health Check tab shows a warning when a data policy blocks the app. The app can't change the policy, so an admin needs to lift the restriction in Atlassian's settings. See Atlassian's documentation on blocking app access.
A space can limit access to specific users or groups. If a space's permission list doesn't include the app user, the app user has limited or no access there. This is most common in spaces that existed before you installed the app, because the app user wasn't part of their original permission list. Without sufficient permissions in a space, Automation actions can fail for the content in that space, and Dashboard and Content Audit statistics may be inaccurate. See Atlassian's documentation on space permissions.
A page restriction limits who can view or edit one page, independently of space permissions, and also applies to every descendant of that page. Restrictions apply to the app user like any other account. A restricted page is excluded from Dashboard statistics unless the app user has Can view access, and from Automation unless the app user has Can edit access. See Atlassian's documentation on content restrictions and on adding or removing page restrictions.
You can fix space permission and restriction gaps in two ways:
- In Standard edition, the Health Check tab finds the gaps and fixes them from inside the app. With automatic fixing turned on, the app also fixes restricted contents for you as it detects them.
- The manual procedure grants the app user access by hand in Confluence. It is the only option in Lite edition, which has no Health Check tab, and the fallback when a fix in the app fails.
Using In-App Health Check
The Health Check tab is not available in Lite edition of the app. Use the manual procedure instead.
The Health Check tab lists the spaces where the app user is missing a permission that archiving, deleting, or fixing restricted contents needs, and the pages and blog posts that the app can't read because of their restrictions. You can fix them from the tab before Automation or a bulk action fails there.
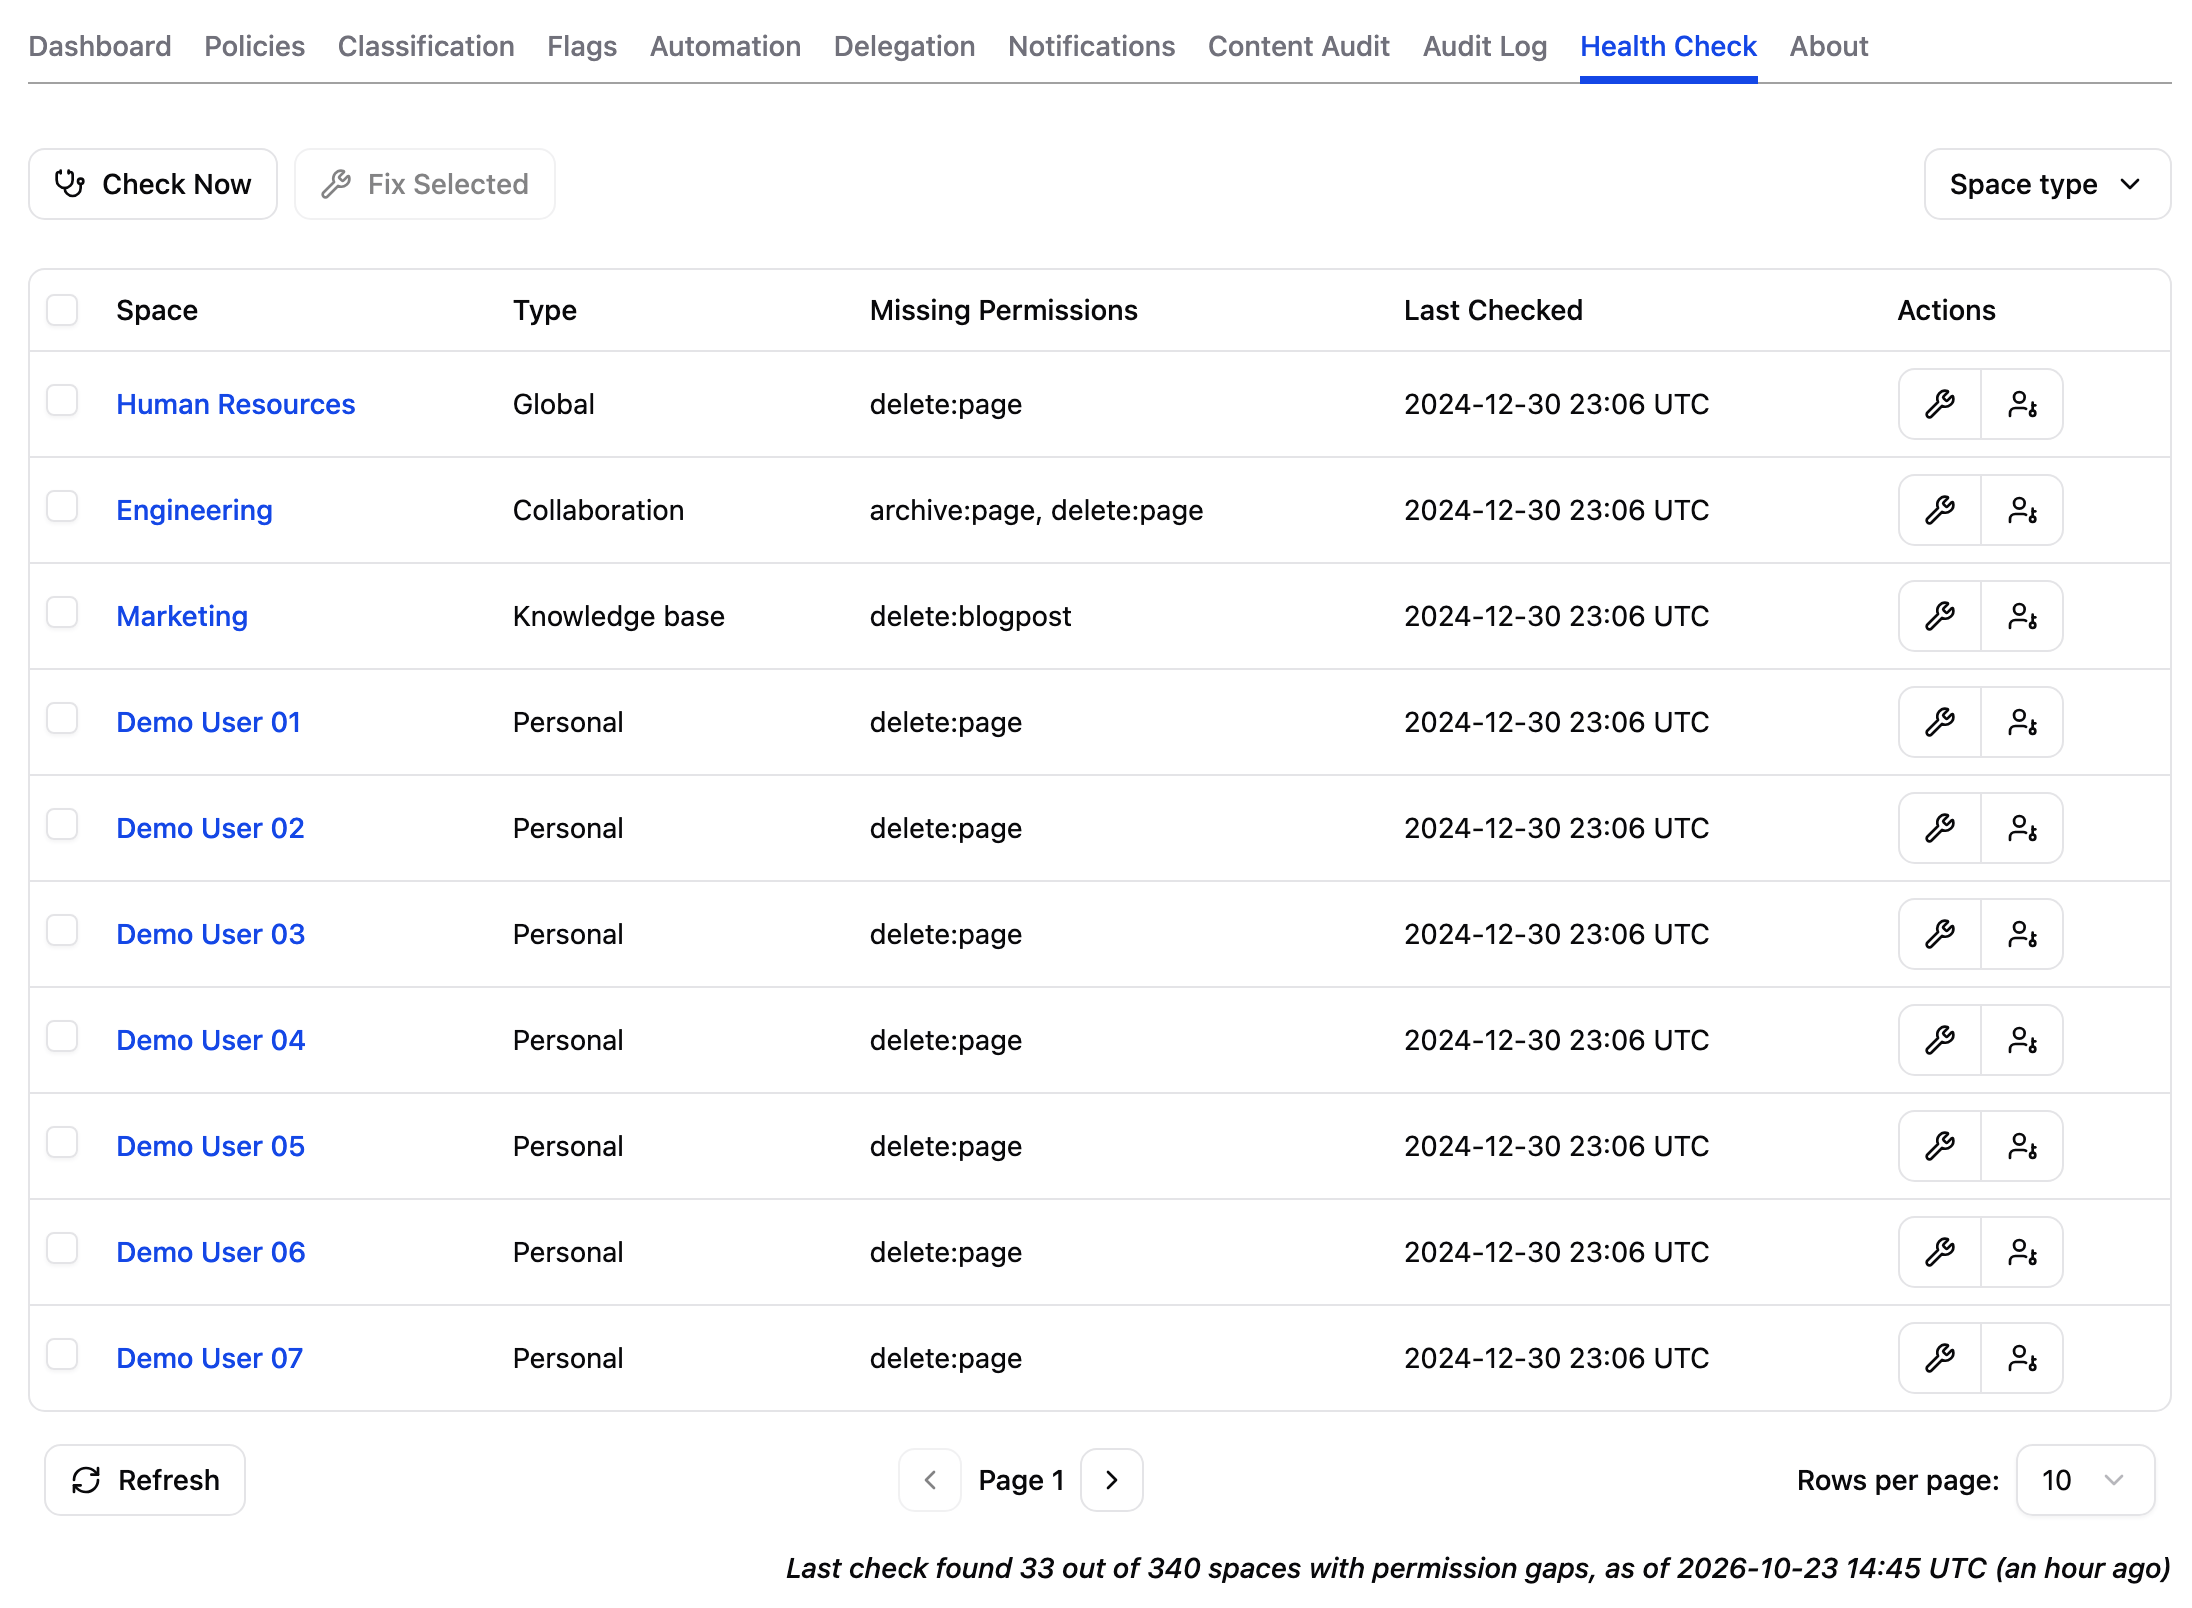
Health Check tab in Content Retention Manager for Confluence
The app scans every space once a day. To scan right away, click Check Now. A scan can take several minutes on large sites, and a Cancel check button replaces Check Now while it runs. Click Refresh to reload the tables and the scan status.
The tab also shows a Data Policy Blocking Content Access warning when your organization's data policy restricts the app's access to some content. Click How to allow access in the warning to open Atlassian's guide to lifting the restriction.
Only Confluence admins can use this tab. Delegated admins see a notice instead, because fixing a gap needs the product's own admin rights.
Space Permissions
The Space permissions section lists the spaces with missing permissions:
- Space: The space, linked to it. A checkbox at the start of each row selects it for Fix Selected.
- Type: The kind of space: Global, Collaboration, Knowledge base, or Personal.
- Missing Permissions: The permissions the app user lacks in that space, shown as keys such as
archive:page,delete:page,delete:blogpost, andmanage_content:space. The last is the Manage user access to content permission, which the Manager role lacks, so a space where the app user has the Manager role is listed here. - Last Checked: When the app last checked the space.
- Actions: The Fix button (wrench icon) and the Open permissions button (person icon).
Use the Space type filter to narrow the list to one type of space.
Click Fix to assign the app user the Admin space role in that space only. Fix runs with your own admin rights and works only on sites that use Confluence space roles. If Fix can't complete, the row shows a warning icon and the Fix button stays disabled until you reload the tab.
To fix several spaces at once, select their rows, click Fix Selected, and confirm in the Fix Permissions dialog. Keep the app open until the fix finishes. Click Stop Fixing to end it early. Spaces already fixed stay fixed. The Audit Log records each successful fix made with Fix or Fix Selected.
Click Open permissions to open the space's permission settings and grant the permissions yourself, as described in Granting Space Access. The Audit Log doesn't record permissions you change this way.
Restricted Contents
The Restricted contents section lists pages and blog posts that the app can't read because of their restrictions. The app can't manage them either, so Automation and bulk actions skip them. See Troubleshooting Permissions for how restrictions affect the app user.
Tip
Turn on automatic fixing so the app adds itself to restricted content as soon as it detects it.
First fix the spaces listed in Space permissions, so the app user has the Admin space role that automatic fixing needs.
Confluence has no way for an app to list restricted content. Instead, Confluence sends the app an event notification when a permission change affects the app user's access to a page or blog post, and the app checks that content. The app also checks content when someone with access opens it. Content that the app can't read because of its restrictions goes on the list. The daily scan rechecks every entry and removes those the app can read again or that no longer exist. See Health Check Limitations for what the app can't detect. Admins also see a notification while they use Confluence, and its Review button opens this tab.
The table shows each item's Title, Type, when the app Detected it, and when it was Last Checked. Use the Content type filter to show only pages or only blog posts.
Click Fix to add the app user as an editor of the page or blog post, using your own admin rights. To fix several items at once, select their rows, click Fix Selected, and confirm in the Fix Restricted Contents dialog. A fix only adds the app user, so nobody else's access changes. The Audit Log records each fix made with Fix or Fix Selected under your name. Click the person icon to open the page and review its restrictions yourself. An item that is restricted only because of its parent can't be fixed on its own. See Content Restricted by a Parent.
Automatic Fixing of Restricted Contents
Turn on Automatic fixing of restricted contents and click Save. The app then adds itself as an editor of each restricted page or blog post as soon as it detects one, so the content returns to retention without an admin acting on it. Turn this setting on unless you want to review each restricted item before the app gets access to it. It is off by default.
An automatic fix only adds the app user, so nobody else's access changes. The app user then appears in the page's restrictions, where anyone with access to the page can see it. See Visibility of the Change. The content the app fixes doesn't appear in the list. The Audit Log records each automatic fix under Automation, and each change to the setting under the admin who made it.
Automatic fixing acts as the app user, so it needs the Manage user access to content permission in the space of the page, and that permission requires the Admin space role. A space where the app user has less, such as the Manager role, is listed in the Space permissions section, so fix those first.
If the app can't add itself, the row shows Auto-fix failed. The Fix button doesn't depend on the app user's space permissions because it acts with your own admin rights, but you do need permission to change the page's restrictions. Neither automatic fixing nor Fix can resolve content that is restricted only because of its parent. See Content Restricted by a Parent.
Health Check Limitations
These limits apply to what the Restricted contents section can list.
What the App Can't Detect
A restricted page or blog post that nobody opens, and that Confluence sends no event notification for, stays undetected. A page restricted before you installed the app, or created already restricted, stays undetected until someone who can read it opens it or its permissions change. The permission change doesn't need to name the app user, but Confluence can take several minutes to send the event notification, and some are never sent. An empty list means only that the app hasn't detected any restricted contents. To look for the rest, use Confluence's own list of restricted pages. See Finding Restricted Pages. The app detects restricted pages and blog posts only, so restricted databases, whiteboards, and folders never appear in the list.
Content Restricted by a Parent
A restriction on content also applies to all of its descendants. For example, a restriction on a page applies to every descendant of that page. A child can therefore be unreadable to the app only because its parent, or a higher ancestor, is restricted. The child appears in the list like any other restricted item, and its row doesn't name the ancestor. Two things set these items apart:
- Confluence sends the event notification for the item whose permissions changed, not for its descendants, so the app finds each descendant only when someone opens it.
- Fix and automatic fixing add the app user to the child, but the ancestor's restriction still applies, so the app still can't read it. The fix is recorded as failed and the row stays in the list.
To resolve it, open the child, find the restricted ancestor above it, and add the app user to the ancestor. See Adding the App User. When the app can read the descendants of the ancestor, the next daily scan removes them from the list. To scan right away, click Check Now. Fix on the ancestor's own row also works, but only if the app has detected the ancestor. The app never adds itself to an ancestor on a child's behalf.
Unpublished Drafts
Only the author of an unpublished draft can read it, so a draft is always unreadable to the app. The app can't tell whether a draft has restrictions. After the draft is published, the app checks the page the first time someone opens it, and detects the restriction, if any.
Fixing Permission Issues Manually
Use the manual procedure in Lite edition, for restricted pages the app hasn't detected, and when a fix in the app fails.
Granting Space Access
To grant the app user access to a space:
- In the space, hover over the space name and select the ••• button in the sidebar, then Space settings.
- Select Users to manage what users can do in your space.
- Search for Content Retention Manager for Confluence (or Content Retention Manager Lite for Confluence for Lite edition), then select the Admin role for the user. The change should be automatically applied and saved.
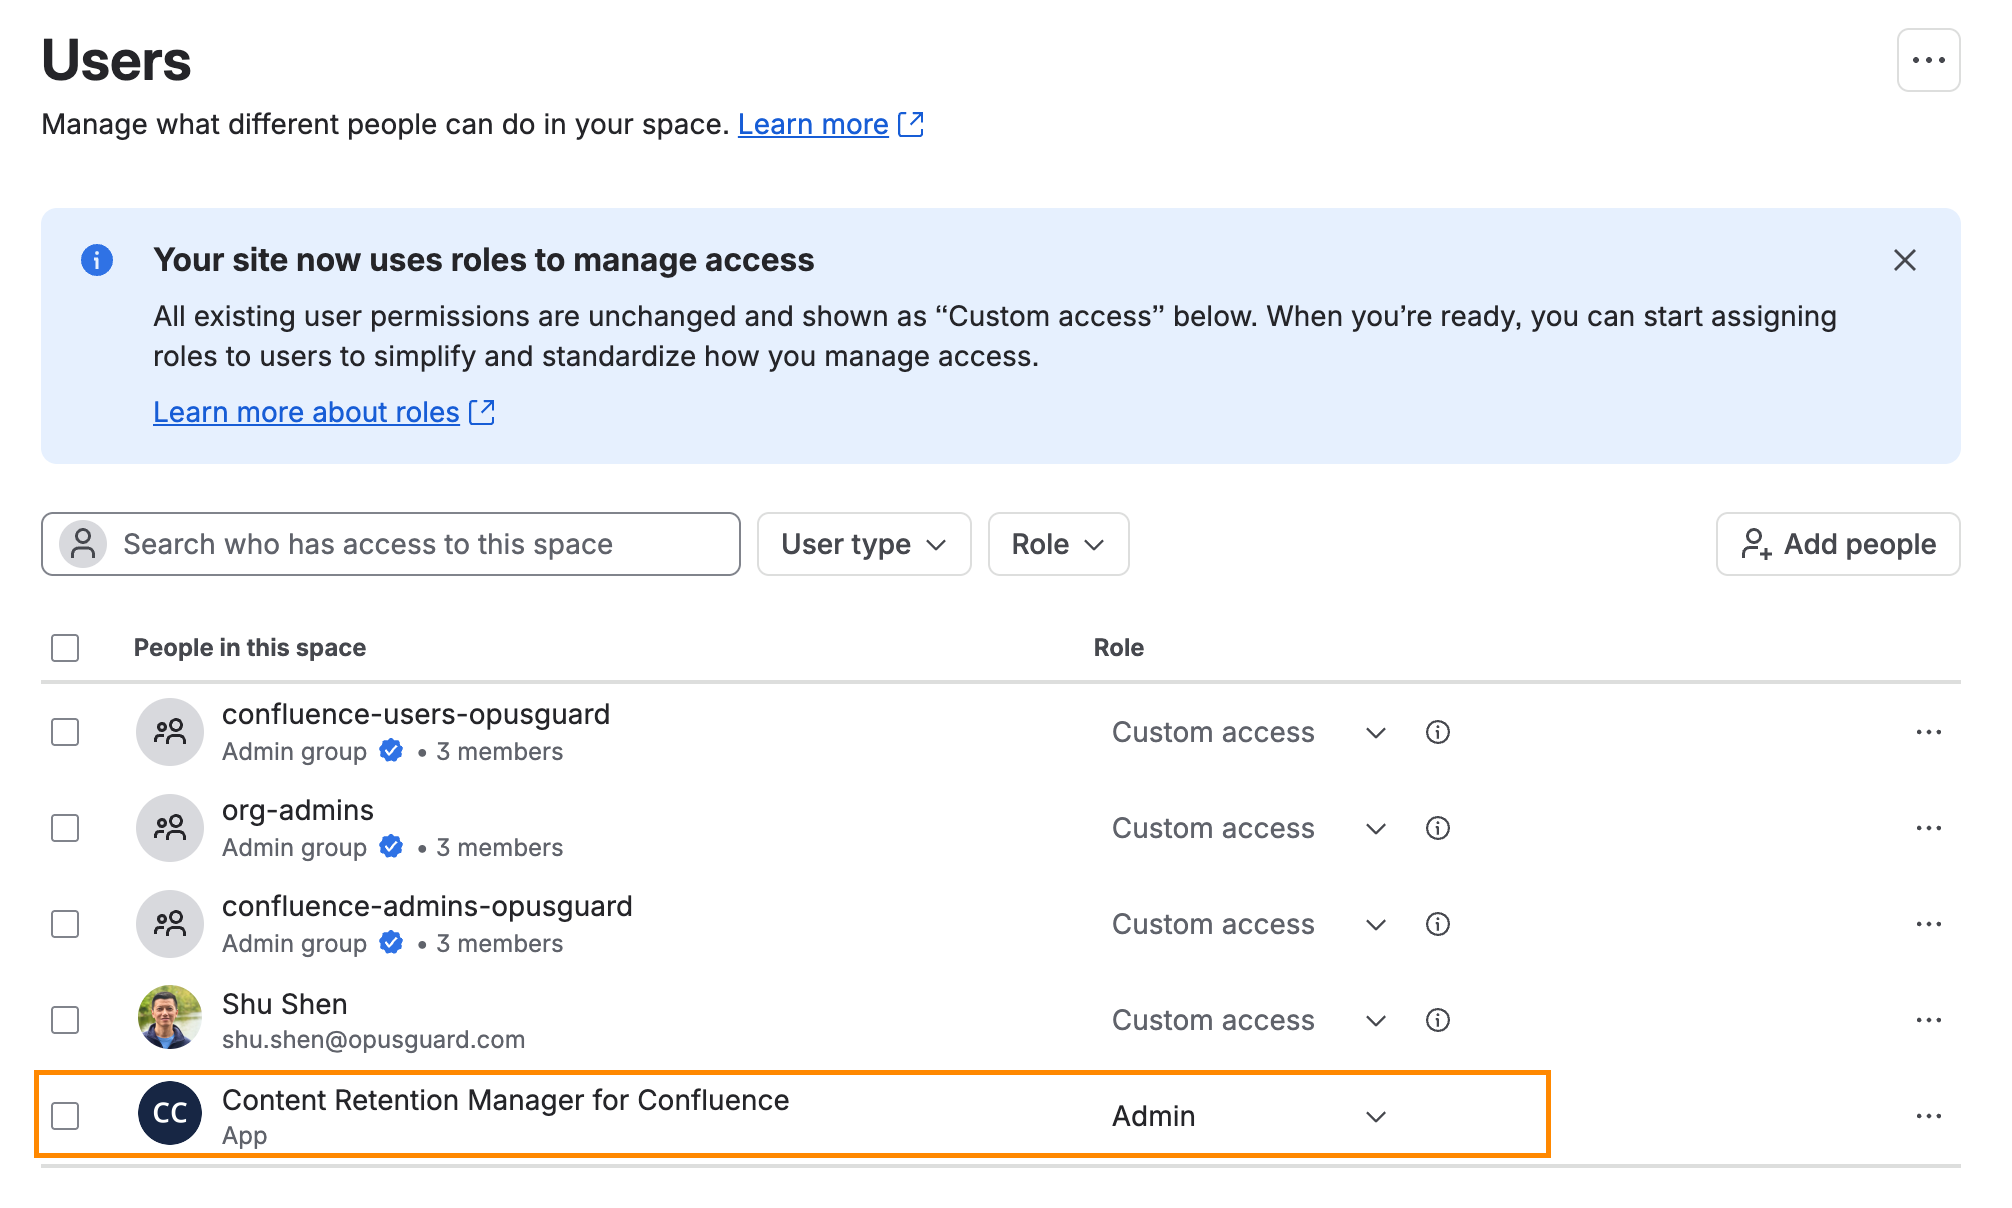
Users in Space Settings controls the role assigned to the app's user
Info
Granting the Admin role above gives the app user full control over the space. To scope this down, create a custom role with only the following permissions, then assign that role to the app's user instead:
- View
- Archive, for archive bulk operation and automation
- Delete, for purge bulk operation and automation
- Edit, for per-content classification bulk operation and from Confluence byline item
A custom role doesn't support automatic fixing of restricted contents in Standard edition. That feature needs the Manage user access to content permission, which requires the Admin role.
See Atlassian's documentation on assigning space permissions for more details.
Restricted Pages
To include a restricted page in Automation and Dashboard statistics, grant the app user Can view or Can edit access to it. The sections below show how to find the page and add the app user. Once access is granted, the page appears in Dashboard statistics and is subject to Automation on its next scheduled scan. Restricted pages appear in the Content Audit only for users who have been granted access in the page's restrictions.
Finding Restricted Pages
Confluence lets a space admin list the restricted pages in a space:
- In the space, open Space settings.
- Select Content, then select Restricted.
Repeat this for each space you want to check. See Atlassian's documentation on finding restricted content in a space. The app can't read this list, because Confluence has no API that lists restricted content for an app. Use it to find the pages the Health Check hasn't detected.
As a Confluence admin on Premium or Enterprise, you can also use your admin key to reach a restricted page without being listed in its restrictions:
- Open the page by its URL. When you open a page you don't have access to, Confluence shows a prompt. Click View now to activate your admin key. A yellow banner at the top of the page confirms it is active.
- Search with the Confluence REST API while your admin key is active. When you include the
Atl-Confluence-With-Admin-Key: truerequest header, the results include restricted pages.

Confluence prompts a site admin to use their admin key to view a restricted page
Adding the App User
With the restricted page open, click the Share button on the page toolbar.

The Share dialog on a restricted page, showing Restricted general access
In the Share dialog, type Content Retention Manager in the search field, select Content Retention Manager for Confluence (Standard) or Content Retention Manager Lite for Confluence (Lite) from the results, set the permission to Can view or Can edit, and click Save.

Adding Content Retention Manager for Confluence with Can view access
Known Confluence issue
After clicking Save, Confluence may show a spinner rather than confirming the change. This is a known issue when an admin adds a user other than themselves to a restricted page. The app user is added successfully despite the spinner.
Reload the page and reopen the Share dialog to confirm:

The Share dialog after the app user has been added, as seen by the admin
Visibility of the Change
Anyone with access to the page can see the change. When they open the Share dialog, Content Retention Manager for Confluence appears listed with Can view or Can edit based on the granted access.

The Share dialog as seen by the page owner. The app user is visible to all who have access to the page.
About
The About tab provides a quick reference for your installed version and links to helpful resources. It displays the app name and version number (e.g., v6.5.0). Use this version number when contacting support so the team can assist you more effectively.

About tab in Content Retention Manager for Confluence
Under Resources, you'll find links to documentation hosted on this site:
- How It Works: Overview of how Content Retention Manager works under the hood.
- Quick Start: Step-by-step guide to get up and running quickly.
- Release Notes: Changelog for all past and current releases.
- Glossary: Definitions of key terms used throughout the documentation.
Under Support, you'll find a link to the Opus Guard Support Portal where you can submit tickets or browse existing knowledge base articles.
Under Feedback, you'll find a link to rate Content Retention Manager on the Atlassian Marketplace.